
Maurice Côté
Add FreshService as ticketing service
Hi,
I have used their contact us form twice and no reaction on my request to onboard their partner program.
If you have a support plan with them, could you ask them for help into onboarding us as a partner, I would give you my email address by direct message if you agree.
Best regards,
Add TOPdesk as a Ticketing service
Hi CC
I do love feature requests
TOPDesk is full ITSM at first glance, but was are your needs? We have three levels of integration
List tickets only
Log work, log comments, transition status (I would hope to have a creation flow as well, surely in the next MAJOR release)
designed on paper, almost ready to start on it : Full ITSM flow validation : "has the CAB approved a change request with a maintenance window active at this time", will likely be linked to our PAM Checkout
Also, what auth model you are using?
Application password + Basic auth - The operator generates one under My settings → Application passwords; the username is the TOPdesk login of the operator who created it. Requires read on REST API and write on Use application passwords in the API Access permission block.
OAuth 2.0 — added in the 2025 updates and positioned as the modern path, short-lived tokens. Existing Basic and application-password accounts keep working; there's no forced migration.
Thanks
Native Palo Alto GlobalProtect VPN Integration
Hi,
Sadly, the client that you use must support some way of automating it, be it a CLI, plain old command line arguments, a SDK, in short: anything that can be used to say "open THAT tunnel with THOSE credentials".
I dug around and the Global Protect ecosystem is quite confusing, I could not make sense of what is current. The image I attach is an AI summary. Some would say that it's AI slop, but I just find it illustrates the complexity of that specific platform.
We'd really prefer to satisfy our customers that ask for an integration, but for that the vendor has to offer the capability.
Be assured we monitor the vendors and will gladly react to implement support if the landscape changes.

Multiple Re-Authentication prompts when switching network
Hi,
Could you try this and let us know?
Connection issues when switching network - Devolutions Documentation
thanks
Multiple Re-Authentication prompts when switching network
Hi Riccardo,
Your account in the forum is recent, but the fact that you say DPS hints that you are an old friend ;)
Can you confirm the versions of both RDM and DVLS. Also, Duo can be setup a few different ways, I have to assume you are talking about this mode
Multifactor - Devolutions Documentation
Please confirm
Thanks
PSM history not incremented with RDM
Hi Philippe,
The fix will be in v2026.1.19, I do not know exactly when it will come out because its not even built internally yet. It will have to undergo testing and so on.
Best regards,
PSM history not incremented with RDM
Hi,
I will discuss this with our integration team. We could either add it to all calls, or expose a setting to let the administrator decide.
The former would take minutes, the latter a few hours.
Support custom attributes in PAM import
Hi Simon,
I will submit the request again to the portfolio committee. Accounts are now full fledged RDM Entities and support hundreds of fields.
Our objective would be to keep this request as simple as possible, we use the “rocks / pebbles / sand” system at that level, so if we can keep it "pebble" size, it would help greatly in getting it done.
We could offer to map a named field like you want, but to our CUSTOM_FIELD_X attributes, would it be sufficient?
e.g. CUSTOM_FIELD_1 : otherPager
My concern is WHERE you want to consume that information: in the PAM discovery dashboard, or simply in RDM. The latter would be easier.
Please let me know
PAM - Approval process only when using JiT Elevation, or choose between PAM accounts on RDP Connections.
Hello,
We have modified the flow to account for conditional access policies that we are introducing, as well as privilege sets to limit groups allowed to JIT for certain users.
I think it would be appropriate to wait for comments on what is coming out in 2025.3 in a few months. I think that your concerns for JIT approval will be addressed
As for the ticket part, we havent modified it yet.
Best regards,
DVLS Synchronizer Schedules
Hi,
I dont know how when transferring the feature from RDM to DVLS the decision was made to only allow it once a day...
I am adding it to our weekly meeting for discussion, my intent is to allow with a granularity of hours.
Best regards
[FEATURE REQUEST] PAM infrastructue deployment PS1 Scripts for users
Hi,
We have a native provider that is meant for 80% of our users, the AnyIdentity provider is to allow users to personalize the various phases.
A session would help confirm what you need
best regards
[FEATURE REQUEST] PAM infrastructue deployment PS1 Scripts for users
Hi John,
It was a priority of Q4 to make easier onboarding, but it’s such a large task that we will be able to do only a little.
Have you asked for a session with our Customer Success team to get you started? They are free…
I don’t know why you chose the AnyIdentity layer to start with, don’t get me wrong I love them, but they are meant for scenarios that our “native” providers cannot achieve.
I have my own set of steps to automate, but we definitely could use everyone’s input to better capture the tough parts and ease your pain.
My intent is to have the product guide you, and powershell available for edges cases. Having a script would be a good start.
We have a powershell guru helping us, we just need to have granular tasks and objectives.
That being said, please reach out to support , I want you to benefit from the product ASAP
Devolutions Password Manager connected to DVLS
Hi Jakub,
This portion of the integration is limited as dictated by the CyberArk team themselves.
The mandatory requirement was to only use privileged accounts with technologies that make it hard to divulge the passwords. This forced us to remove a long list (PowerShell, Command Line, Web, etc.) of our session types. We can only use protocols that allow for "secure credential injection", meaning that the password is likely set directly "in memory" in the connection.
This requirement by the CyberArk team was pretty hard set, they are pushing for privileged sessions through their PSM and they prefer that the passwords never exit from that environment.
Sorry about that, but we cannot implement this request.
Best regards,
Limited PAM Administrator
Our own team asked for this when we gave them our PAM initially.
We have a huge undertaking of harmonizing our PAM with the RDM architecture. We are hoping to finish the project by the end of the year. Once that is done, we can finally think of reworking the permissions. Its always been a let-down for me to only see the PAM under the Administration menu. I cannot wait to separate the functionalities per area of concern instead.
Sorry about that
Connection to JIRA
ah yes!
You make me happy, I am adding this in RDM as we speak, but sadly I started with ServiceNow...
My belief is that, for many orgs, EVERYTHING starts from a ticket. So we would have a dashboard that would allow for opening your tickets list, add notes, and even transition them to another state.
That's what I would implement in the first phase, but we are dreaming of having the target session selected in your treeview, even up to the privileged account to use if you use our PAM module...
Since I'm coding only part time, it does take more time for my stuff to make it in production.
I'll try to see about doing Jira quickly
PAM Providers shared between devices
Hi Andrew,
The providers are meant to be linked to a source of accounts, and each device in itself is an Identity Provider. We also have to remember, for those that want to attain it, the Zero Trust requirement of never reusing the same credentials, all at the same time protecting the devices by monitoring new accounts/keys created without authorization.
That being said, we realize there is friction when managing multiple non-federated devices (we experience the same pain, I can assure you). We would need to find way to onboard a great number of providers, and to simulate that the devices are federated. Francois mentioned what we had done for Active Directory joined computers, we could present, lets call them sub-providers, in a similar fashion maybe...
For the onboarding, we could use the PAMAdmin account that you provision on all devices to create a unique one to replace it.
All of that to say that we are suffering from the same pain, trying to find a solution that checks all the boxes, and hopefully we'll come up with a good solution.
Best regards,
SAML 2.0, or OpenID Authentication
Hi Javad,
We will let our customers share their thoughts.
Please contact me by Direct Messaging if you feel the need to add to this discussion.
Best regards,
SAML 2.0, or OpenID Authentication
Hi Javad,
Since you are representing your company that does offer an IdP, I can understand your viewpoint.
But for our customers, the reality is that simply integrating IdP using SAML/OIDC is insufficient. The great majority requires group membership as well in order to run our RBAC. Sadly, that part of the standards is nothing but standard and we need to customize for each and every IdP.
Because of this fact, and also because we are driven by our customers' requests, we only implement vendors that are requested by the community.
Best regards,
Additional options for password rotation schedule
Hi Jonathan!
Thank your for taking the time to submit a request, I'll open the ticket since it makes a lot of sense and is perfectly aligned with our goals.
Please be aware that we are closing version 2025.1 as we speak, and v2025.2 has a lot of stuff already planned...
I hope it's added soon!
Copy PAM Password to Clipboard takes long
Hi Philipp,
Since the password, in the case of PAM accounts, is only decrypted JIT with the help of the server, and the server needs to validate the checkout settings, approval, etc., its normal that it takes longer, but I admit that 5 seconds seems a bit too much.
I will open an issue on our end so we validate that whole path of accessing the password.
That will hopefully take care of our side of things, but on your end, is the server responding with acceptable performance when opening a vault?
thanks
Damware Mini with PAM
ok, I will ask someone to look into this
Damware Mini with PAM
Hi,
Sorry about the delay.
We've added "Usage policies" to allow you to specify where privileged accounts could be used.
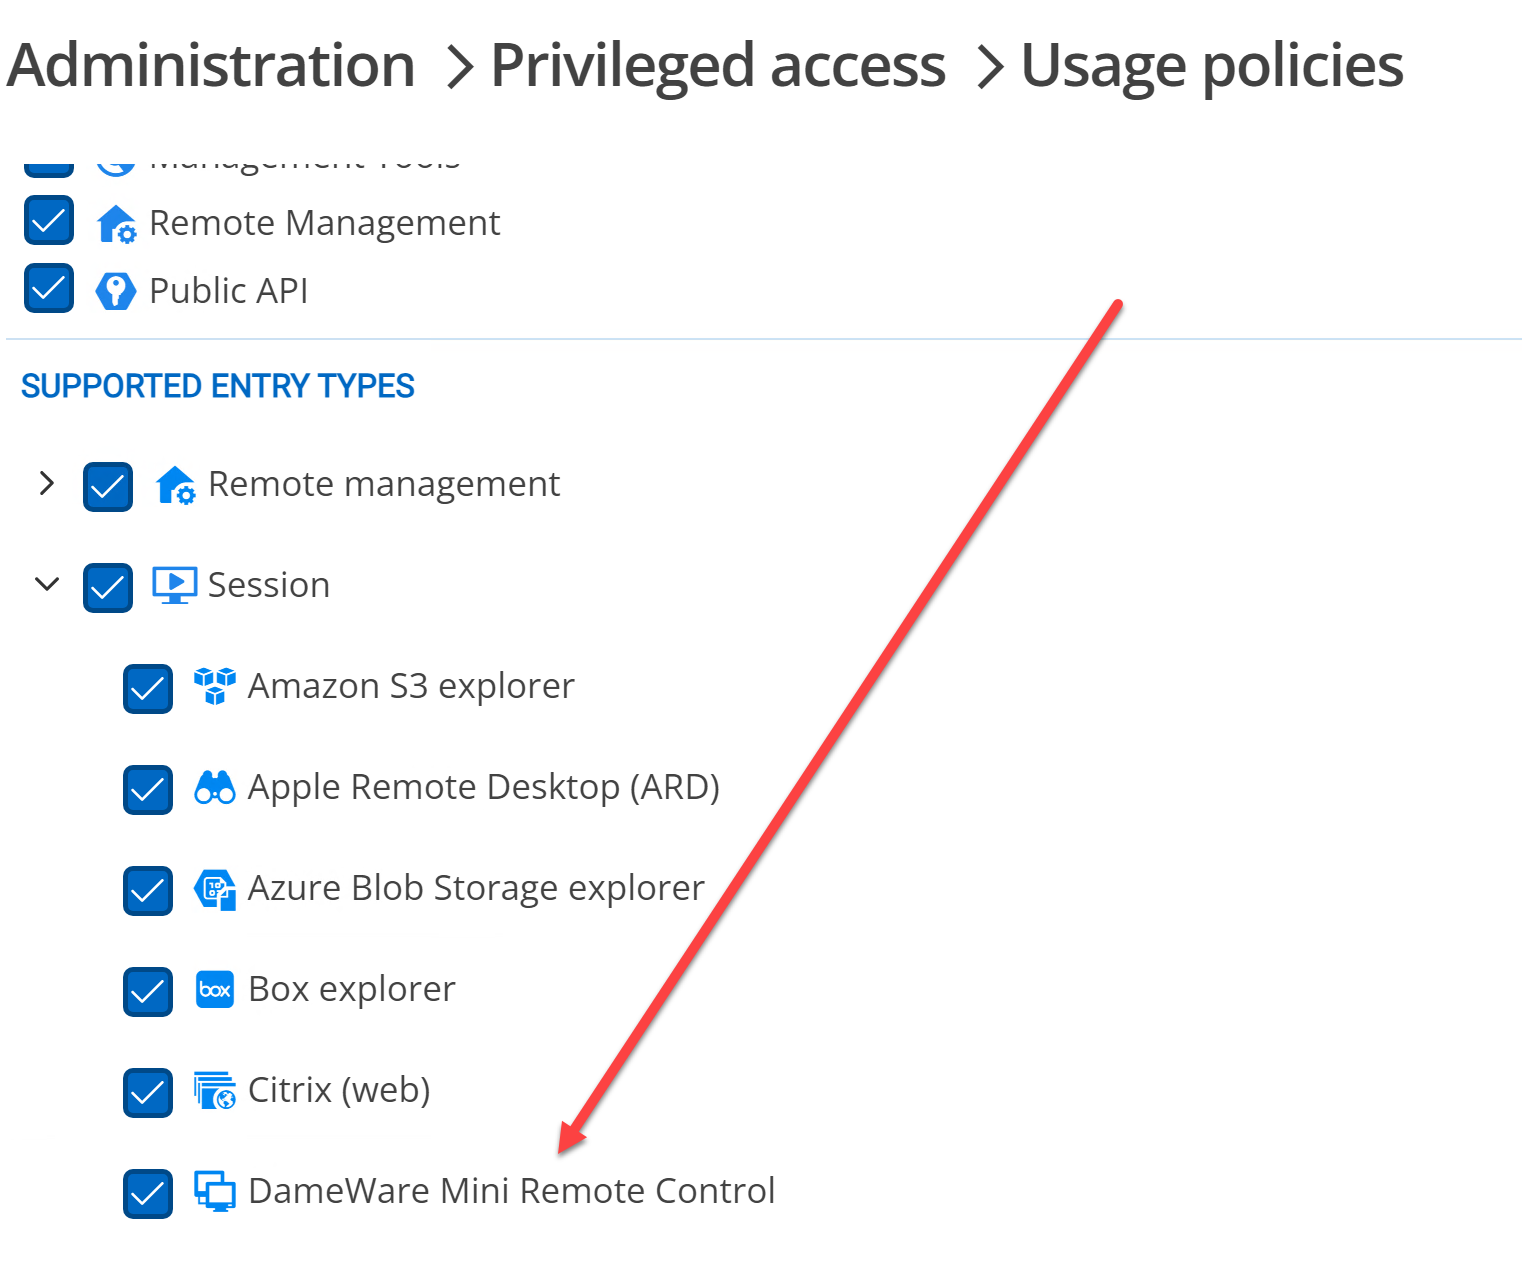
Is this turned on?
Best regards,
Feature Request: Variable Password length in Password Generator
Hello,
First let me apologize about the delay.
I will open a ticket but I'm curious, is this to make brute-force attacks tougher or is there a compliance requirement that recommends that?
Thanks
Constant Crashing when closing terminal sessions.
Hi,
I think that the "Wait progress mode" option was created for the few users that had that type of issue a few years back, set it to status bar for the intended workaround.
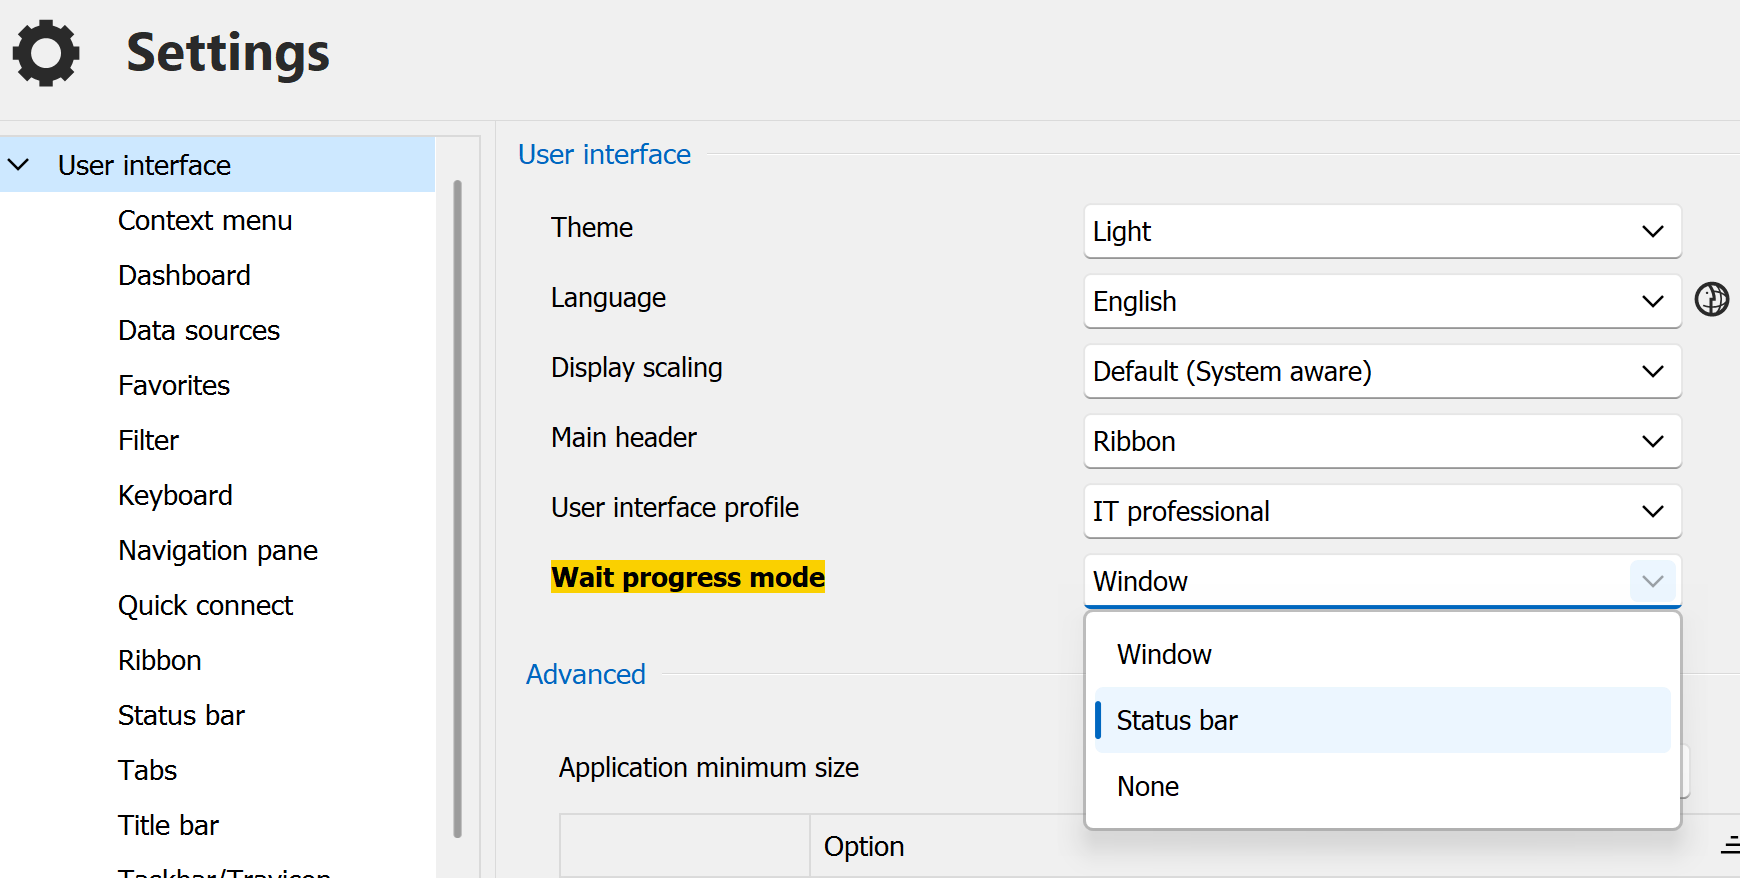
You will need a few days to get used to looking in the status bar but some users even prefer it.
edit : added the name of the option and fixed typos
Please let us know how that works out.
Ribbon bar missing
hello,
please try Window - Reset layout as per