
miccol
Change when "All Devolutions Gateways in the farm are down" is shown to users
Hi there.
We have a couple of Gateway sets that are running HTTP (yes, something to improve, I know) - This results in the users being presented with a Gateway set that reports "All Devolutions Gateways in the farm are down"
If I check the Gateway set in the backend I can see the same, but if I then expand the set, I see "Gateway is configured with HTTP. Secure HTTPS communication should be used"
Users are unable to expand the set and see that the error is actually caused by not running HTTPS but HTTP instead - This confuses the users which I'd like to avoid.
Could something please be improved here?
Thank you
Allow "Clear cache" configuration on web frontend
Hi
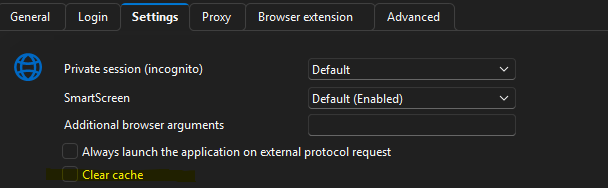
We have a bunch of people using Devolutions Launcher. Among other things, they use it to access webpages and apparently the WebView2 cache becomes a problem over time. In RDM we see the "Clear cache" setting which we assume clears the cache every time the webpage is either launched or closed...could this option please be made available to be configured via Web frontend as well?
Thank you
User notice when recording is configured
I'll keep the workaround in mind, it's definitely something we can use in other regards.
Thank you for opening a ticket, looking forward to the feature.
User notice when recording is configured
Hi Hubert, thank you for your response.
We're predominantly using Devolutions Launcher for external vendors and those internally that only access a couple of servers. Some of us are using Remote Desktop Manager tho, but the solution would have to be something that users can't modify themselves...even users with write access to the vault I need to restrict from removing the message.
If I can configure something in the backend or even on a vault level, that would be nice, but it has to work with Launcher as it is our go-to tool.
It's a legal thing basically - Users have to be informed that their session is recorded so they can decide if they wish to proceed or simply not proceed with their session.
User notice when recording is configured
If not possible already today and I've missed something, would it be possible to add a feature so that the user is prompted with a custom prompt for session recording? Maybe something designwise similar to the prompt you get for PAM checkout. I'd like to inform my users that they're starting a session that is recorded and that if they disagree with this, close the session.
Thanks.
Allow PAM checkout via Launcher
Exactly what I was looking for! Apologies.
Thank you!
Allow PAM checkout via Launcher
From Launcher, if I double click a server, I'm presented with the PAM checkout window which works fine. The issue we're facing is that there is no way of building in a "delay" of sorts to allow for the JIT user to be created or JIT groups to be assigned and therefore the first login fails. The user has to wait a minute or so before they attempt a reconnect and everything works.
I would like to request 2 things here...one being the possibility of the user right-clicking the PAM credential set and then checking out the account first, before logging on. The other being the ability to build in some sort of delay, similar to when using Jump to a server - The delay feature would also be relevant in RDM.
Thank you
Sync licenses with Entra ID group membership
Hi
I'm not sure it's working as intended.
This is my config:

Yet when I join an existing user to my Entra ID group that should assign a license to the user, it does nothing. I added a user to the Entra ID group earlier today but it's not working.
It's as if it only applied a license when "creating" the Devolutions user IF the user is at that point a member of the Entra ID group.
Sync licenses with Entra ID group membership
If I'm missing something, i apologize, otherwise I'd like to have something along the lines of the following:
All users in our organization are able to access Devolutions Server via SSO and most don't have the need for any other license than WFM. We administer our licenses via en Entra ID group that has been enabled for auto-assign...my issue is when a user logs on to Devolutions Server prior to being a member of the Entra group that grants a license for e.g. Devolutions Launcher...The fact that I then add them to the Entra ID group does nothing within Devolutions.
Would it not be possible to enable some sort of sync from Entra ID that runs at an interval? That way I would be able to simply add the user to the Entra group and wait 5-10-15 minutes for the sync to happen and then a license is added to the user.
Hope the above makes sense :)
Thanks.
Customise Devolutions Send
I've actually had a few users delete the email they received and mark it as phishing/spam because it didn't look like something they would expect to receive...
So whatever can be done to allow us to configure it to look and feel "safe", that would be nice.
Allow Doubl-click on action configuration in Devolutions Launcher
Cheers! I'll pass that information along. Do let us know when added to Launcher. Thanks.
Allow Doubl-click on action configuration in Devolutions Launcher
Hi there
Would it be possible to include the highlighted configuration from RDM in Devolutions Launcher as well?
Thanks /Mickey

Add website proxy configuration as configuration on Web
Hi Marc-Andre
I'm the man in the middle here, requesting on behalf of some of my administrative users.
I've been given the following explanation, hope it helps out:
"When we use a link "Web places" accessing a webpage internally, we normally can use a http proxy
like the below example, if you run it manually:
curl -ki 'https://domain.local' --proxy http://server.domain2.local:447
When we configure "Web places" we have no a choice for configuring http proxy"
Thanks
Add website proxy configuration as configuration on Web
Hi there
We have quite a lot of users using a combination of Web/Launcher and they're quite often missing configuration options that are currently present in Remote Desktop Manager.
Could more features please be allowed configurable via web? In this case, the Proxy tab from RDM is the most pressing one for us.
Thank you
PAM vault not showing as a separate tab any longer?
Hi Tommy
Yes, I'm referring to the "Show PAM vault tab" below. Just not sure what this does if not what I'm thinking.

PAM vault not showing as a separate tab any longer?
Hi Erica
Thank you for your response. Yes, I've also found the privileged accounts there, but I was hoping that the checkbox mentioned would place it on the tab bar - Otherwise, could you explain to me the point of the checkbox?
Thanks
PAM vault not showing as a separate tab any longer?
Since a few versions ago in RDM it seems that I lost my PAM vault button in the Navigation bar (next to User vault) - I see in settings there is a setting for this, but it's as if it does nothing.
Anyone else experiencing this?
Add "Allow any additional hosts with Devolutions Gateway" as configuration on Web
Just fantastic service! Thanks.
Add "Allow any additional hosts with Devolutions Gateway" as configuration on Web
Hi there
I see the following added a while back: "Allow any additional hosts with Devolutions Gateway" option in website connection settings"
This is a great option yet only configurable via RDM - I expect/hope that while the option can only be enabled via RDM, it actually works via Launcher as well.
Please make the option available to be configured via Web, so it can be used with Launcher as well.
Thank you
RDM error "Request failed on background thread."
We too are having this issue.
We have a load balancer in front, 4 webservers and a SQL always-on backend.
"Use X-Forwarded-For" is already enabled.
We're running 2025.3.11.0 and 2025.3.26.0
If we can help the resolution of this by supplying some logs, please do let us know which to gather.
Thanks.
Import Azure AD groups
Cheers, that works! :)
Import Azure AD groups
Hi Patrick
Thank you for your reply.
Not entirely what I'm looking for.
When I go and create a new vault, I'd like to fully automate this process. High level this process is:
Create Entra ID groups
Import Entra ID groups to Devolutions
Create vaults and assign permissions
It's the 2nd step I'd like to figure out if I can somehow automate...either via some PS or API call or something.
Import Azure AD groups
I'm trying to fully automate the Vault creation process.
To grant access to vaults I use Entra ID groups.
When creating new vaults manually, I simply go to User Groups, hit "Import" then select "Azure Active Directory", filter for a certain name standard and then hit import.
I then go about assigning permissions later on.
I'm struggling to figure out how to automate the step above. Creating a vault is easy, assigning permissions likewise, but importing Entra ID groups...how to do that?
Thanks.
Customise Devolutions Send
I second this, some sort of branding possibilities for Devolutions Send would help increase the legitimacy when sending out secure messages.
Devolutions SEND Enhancement Request
Hi François
Sounds great about the branding, I'll add my voice.
Regarding password generation, I basically just throw it away - It's quite common that users need their password reset and for various accounts we don't allow selfservice.
This would be a much useful feature for our support staff.
Thanks.