
john.kenny
Sysadminotaur #167: Return of Pow3r U53r 78
If only they knew how much is involved lol....
Sysadminotaur #169: CTRL+ALT+DELEGATE
LOL, been there...... nowadays just keep up to date is full-time job...........
[FEATURE REQUEST] PAM infrastructue deployment PS1 Scripts for users
Hi John,
It was a priority of Q4 to make easier onboarding, but it’s such a large task that we will be able to do only a little.
Have you asked for a session with our Customer Success team to get you started? They are free…
I don’t know why you chose the AnyIdentity layer to start with, don’t get me wrong I love them, but they are meant for scenarios that our “native” providers cannot achieve.
I have my own set of steps to automate, but we definitely could use everyone’s input to better capture the tough parts and ease your pain.
My intent is to have the product guide you, and powershell available for edges cases. Having a script would be a good start.
We have a powershell guru helping us, we just need to have granular tasks and objectives.
That being said, please reach out to support , I want you to benefit from the product ASAP
@Maurice Côté
Thanks for the reply, I may try support see how get on. Also regarding what you mentioned about AnyIdentity, seems i assume yet again wrongly lol (one day I might learn to stop with my assuming with everything) bit I mistakenly took AnyIdentity as your umbrella term for any Identity providers that were customisable configurations, additionally i also used the templates from the github repo called anyidentity..
Anyway I'm using the provider template for EntraID is that right then?
Thanks
[FEATURE REQUEST] PAM infrastructue deployment PS1 Scripts for users
Ive had PAM running a few months back and started making use of it, till one day everything ground to a halt, after going through documentation (which is always being updated, although sometimes it lags behind the software I've found) as well as using the forums for help, but I still don't have a working PAM...... So now I've planned to take a fresh start approach to PAM and its setup, the AnyIdentity Provider for EntraID, the EntraID Applications, the App credentials for DPH bus and then the PAM Service module on windows.
It made me think boy this would be so much simpler if there were a PS1 that would at be able to assist in the infra setup, it could prompt for variables where needed then it would setup the EntraID provider file, the EntraID app registrations and permissions etc, create the DPH app creds again prompting for scenario path choices, then saving the app creds ready to use with the PAM service module that the user can install.
I realise this takes work from the Devo Teams whom are probably already working flat out on other tasks, but they have done this sort of thing in the past so for any season PowerShell gurus with knowledge of Devolutions apps it shouldn't take too long right??
So yeah that would be my wish a PS1 that is able to help us setup the every growing in complexity PAM app using prompts for different scenario path choices......
[ISSUE] DPH PAM Service module stopped working?
No, so no error anymore, so the original error most likely was linked to using Reporting in the Service perhaps without the DPH PAM app permissions set, I think Im going to start over from the very start, dump PAM resources from Entra, DPH and RDM and start over, hopefully the Docs on Devo have caught up with the releases and see how it goes, as now i see an EntraID cannot reach error which I know for a fact was working when I originally posted about the RDM error lol...
Think Ill post a Feature request while I'm at it for DPH or the Service to be able to generate PS1's to setup EntraID and DPH app creds for the PAM service..... (don't mean to create more work but I've had nothing but probs every few updates using PAM to the point I'm thinking about dropping to come back at future date...)
[ISSUE] DPH PAM Service module stopped working?
OK so looks like the dual loop is because I'm selecting the multiple functions of the service which I didn't know before, although I'm about to count the loops with all 3 now, where are the hub service functions designated on hub administration or is that done via permissions? I'm just wondering why a single app cred cant do all the services jobs, I do understand why It would but it would be handy to be offered another option regarding the use of separate app creds in the installer if we wanted too.....
Right so installing the 3 functions it does the double look for app creds then it asks for a url and port for the encrypt service which I've no idea where to point too, so that answers my original question. If the documentation has been updated so that it mentions the use of separate app creds for PAM and Reporting then I missed it again, although I cant say I've every noticed the extra parts including where to point the Encryption part to URL and Port?? Also, remember I mentioned this but I did start with PAM working and not changed when It originally stopped working which after that point I've not been able to reinstate it. I will take a look but the latest version seems doesn't loop extra when Encryption is installed so my query has mostly been answered regarding the looping.
To add, does look like the Docs DO NOW show the separate app creds on different pages, I'm going to try PAM in RDM with just PAM running to see if I still see the original error.
Thanks for that,
[ISSUE] DPH PAM Service module stopped working?
@john.kenny
But the installer form for the details is still looping twice and its done that the last few updates, which is very annoying,
That's strange, we've never reproduced that internally, could you send a video of the behavior? (Without any sensitve information) at https://devolutions.sharepoint.com/:f:/s/SessionRecordings/EiYJqpvo4F9FhZFOth2eHPEBW-uH5zBus7dMnKain4NOvw the 1 prompt per service is normal as you'd have to create seperate app user credentials for each, but more than that isn't.
Ive uploaded the info, does PAM and Reporting in the module need different app creds then??
Would that be why its looping twice? Although I notice that if i select PAM and Reporting it loops twice, if i select all 3 inc Encryption then it loops 4 times, so that could explain the extra loop of the duplicate loop
Anyway, this try with PAM I ran into yet another issue, there must been a change I hadn't noticed regarding Approver members? I have 2 checkout policies for my PAM with each set on 2 folders in the PAM vault, one folder I use checkout approvals the other I don't, both also allow users to approve themselves and provide a reason as an optional. Well I received an Error prompt again, this time from what I could pick out was not having any Approval members?? But it did the same for both checkout policy paths, which confused me further seeing as one policy I've tried to set to not need any additional inputs as there for my main tenant creds where as my other policy is for my 365 dev tenant I use...
I'll look into this and get back to you, this is with the latest PAM service version 2025.1.500 correct? Could you also provide the error you are getting?
Latest PAM service yes
once I pass the member error the 2nd error is still the same as it was before,
On this topic has RDM still not rolled out that Linked creds (External Vault) feature yet, I've been looking for it but haven't noticed it yet.
The new Linked Credential (External Vault) is only supported in RDM with SQL server at the moment, we're working on getting available using DVLS and Hub.
Thanks
@Luc Fauvel
Standalone – Restricted users
Good Morning to all
This is an interesting topic.
I actually have a similar request what concerns Gateway WebUI Access.
For the moment it can be configure with a user.txt but it would nice to have an option to allow the users dynamically from the users groups created in Devolutions, such as Local AD or Entra ID.
This would allow easy user management and the possbility to use a WebUI to access resources.
If this feature is already available, I apologize for the "bump" to this topic.
TY in advance.
Have all great day.
BR,
Greg
@GGORG
Hi gorg, you probably jumped in on my Feature request down stream a bit as that was my big request as per above, that as mentioned looks to be slowly coming to life thanks to the team who queried my wants in detail in past posts above and look to have been delivering most parts.... 👌👍 Although, I'm only making educated guesses from my very very limited coding knowledge to come to all these assumptions which could be completely off base lol.
But every now and then ill checkup on the repo and go through the commits etc and going through the changes. Rust defiantly isn't in my wheelhouse of skills, only Python, so again, I'm going by educated guesses.
I would like to ask how much of what's in the repo is now usable with current public PowerShell modules / PSRepo releases?? I do really need to revisit my PowerShell 101 again I think, as I would need to use PowerShell's help related cmdlets / cmds to actually work that question out myself without extensive documentation on the PowerShell modules / PSRepos from you guys, Although, being as lazy as I am, Ill prob let GitHub Copilot decipher the repo for me which gets better every week.....
Thanks for you reply and the info regarding the user config txt file👍
[ISSUE] DPH PAM Service module stopped working?
apologies for delayed response, I think the PAM module service finally took the App creds well i didn't see the crypt errors this last time round. But the installer form for the details is still looping twice and its done that the last few updates, which is very annoying, you fill out the host url, ID and SECRET hit test or just next and you lose the field data lol, but the 2nd go it works fine lol...... Also the last time i installed I installed all modules PAM, Encryption and Reports, normally I skip the Encryption component, but installing it caused a the double loop to occur twice lol so 4 times I had to enter the field data this go. You may need to look into that as I've clean installed win 11 twice over last couple months and its always don't the same so I can rule out my install at least.
Anyway, this try with PAM I ran into yet another issue, there must been a change I hadn't noticed regarding Approver members? I have 2 checkout policies for my PAM with each set on 2 folders in the PAM vault, one folder I use checkout approvals the other I don't, both also allow users to approve themselves and provide a reason as an optional. Well I received an Error prompt again, this time from what I could pick out was not having any Approval members?? But it did the same for both checkout policy paths, which confused me further seeing as one policy I've tried to set to not need any additional inputs as there for my main tenant creds where as my other policy is for my 365 dev tenant I use...
So long story short I've had to snooze using PAM now so I can just use RDM without issues using user vault cred searches. On this topic has RDM still not rolled out that Linked creds (External Vault) feature yet, I've been looking for it but haven't noticed it yet.
Thanks
[ISSUE] DPH PAM Service module stopped working?
You can change the application identity values by opening the file in C:\ProgramData\Devolutions\Hub\PAM Service\appsettings.json
As for your issue, just off the logs you provided we can't really tell what might be the cause and we cannot reproduce internally. However, in the appsettings file, you can change the log level from Information to Debug, this will allow us to see in more detail what the issue could be.
Best regards,
Luc Fauvel
@Luc Fauvel
Will give that a go....
Thanks
PS. Sorry got another completely diff topic again soz, only simple one this time. I am using the latest RDM beta but i keep seeing a notification banner telling me that my RDM and DPH data versions are out RDM wants 2025.2 but my DPH is 2025.1, normally that gets updated after an upgrade on startup doesn't it. Any idea why that didn't happen this time?
[ISSUE] DPH PAM Service module stopped working?
I did and have checked and double checked I'm using the right fields, i use the downloaded app id pdfs from my hub that plainly shows the field name and value which match up exactly with the hub service installer (side topic, is there a pwsh cmd to change the hub service app id values? I've been uninstalling and reinstalling to change values which is long so wondered what the alternative is), should I still try reversing the values then or not, also just so you know it was running so was setup correctly but recently I performed a clean install and since then haven't been able to regain the connection. What else should I try? I've gone through the docs for setting this up and setup a new app id tied to my PAM service on hub, but for whatever reason my hub service just isn't able to speak to my hub instance?? I have also used Sysinternals TCPVIEW and was able to see the service contact an IP so i'm assuming its making a connection to hub instance, so from your reply guessing its authentication related issue.
If you have any other suggestions please provide.
Thanks,
[ISSUE] DPH PAM Service module stopped working?
I cant remember exactly when it stopped working but its been a few weeks now and since then ive tried reinstalling the MSI or upgrading to new versions, also added new Application Users with the required permissions. But still for some reason my local Service is failing to make contact with my DPH Bus instance, Application Log Event Errors im seeing are:
Category: Devolutions.Hub.Services.Business.Services.HubContextService
EventId: 0
Error : Hub Key could not be decrypted. ManagedError :
InvalidParameter
===Original Message===
Exception of type 'Devolutions.Cryptography.DevolutionsCryptoException' was thrown.
Category: Devolutions.Hub.Services.Pam.PamBackgroundService
EventId: 0
[Devolutions Hub PAM Service] Could not connect to Devolutions Hub. Make sure to configure your Application User properly in the installer.
Like I mentioned I tried reinstalling and recreating the App Users after seeing these errors but it hasn't helped.
Any Ideas
Thanks
[ISSUE] RDM 2025.2.6.0 beta launch errors then loses licencing assignment?
Sorry for the delay, but as expected it worked on clean W11 instance,
Got another question though, how long tilll credentials linked between vaults is released for datasources other than SQL?
Thanks,
[ISSUE] RDM 2025.2.6.0 beta launch errors then loses licencing assignment?
If it's necessary i can PM a shot, but it gets past datasource and licence loading parts, so I see everything ready to go, just can't click anything at all?
TBH, I am wondering if my W11 instance has past the point of no return to be clean reset......
I'll try my .cfg on a vm to test...
I'll get back to you......
[ISSUE] RDM 2025.2.6.0 beta launch errors then loses licencing assignment?
Maxime,
Good news, it launched at least, then it froze and still is after the datasource has loaded??
Any suggestions??
[ISSUE] RDM 2025.2.6.0 beta launch errors then loses licencing assignment?
Whats the method of dropping the datasource from rdm without touching any other config, I've had a similar situation in the past but no doubt changes since then means it won't be the same resolution, it's one of the files in rdm right? Just thought I'd give it another go reinitialising the datasource once launched.
Alternatively, I'd be happy if you could pm me an early build of 2025.2.7+ if give it a go as I was looking forward to those additions.
Thanks
[ISSUE] RDM 2025.2.6.0 beta launch errors then loses licencing assignment?
I grabbed the beta as soon as I saw the rls notes pane in RDM, i performed an upgrade with the MSI and launched but I ran into errors, see below, after OKing the 1st error window RDM launched the data source web page DPH bus in my case and landed on the licences view, I OKd the 2nd and 3rd errors then RDM informs that it has not Ent licence and stops responding?? Any suggestions as the licence is assigned and valid, is there a file somewhere that would clear this without losing any configs?
at Devolutions.Hub.Clients.HubClient.ReadObjectResponseAsync[T](HttpResponseMessage response, IReadOnlyDictionary`2 headers, CancellationToken cancellationToken)
at Devolutions.Hub.Clients.HubClient.GetHubTransactionStateAsync(CancellationToken cancellationToken)
at Devolutions.Hub.Clients.HubClient.<GetHubTransactionState>b__490_0()
at Devolutions.Hub.Clients.HubClient.GetHubTransactionState()
at Devolutions.RemoteDesktopManager.Managers.DevolutionsHubDataSourceManager.GetSystemSettings(Guid dataSourceId, HubConnectionDataSource dataSource)
at Devolutions.RemoteDesktopManager.Business.DataSources.HubConnectionDataSource.GetDataSourceSettings()
at Devolutions.Hub.Clients.HubClient.ReadObjectResponseAsync[T](HttpResponseMessage response, IReadOnlyDictionary`2 headers, CancellationToken cancellationToken)
at Devolutions.Hub.Clients.HubClient.GetHubTransactionStateAsync(CancellationToken cancellationToken)
at Devolutions.Hub.Clients.HubClient.<GetHubTransactionState>b__490_0()
at Devolutions.Hub.Clients.HubClient.GetHubTransactionState()
at Devolutions.RemoteDesktopManager.Managers.DevolutionsHubDataSourceManager.GetSystemTransactionStates(Guid dataSourceId)
at Devolutions.RemoteDesktopManager.Business.DataSources.HubSecuritySubDataSource.GetCacheID(CacheName cacheName)
at Devolutions.Hub.Clients.HubClient.ReadObjectResponseAsync[T](HttpResponseMessage response, IReadOnlyDictionary`2 headers, CancellationToken cancellationToken)
at Devolutions.Hub.Clients.HubClient.GetHubTransactionStateAsync(CancellationToken cancellationToken)
at Devolutions.Hub.Clients.HubClient.<GetHubTransactionState>b__490_0()
at Devolutions.Hub.Clients.HubClient.GetHubTransactionState()
at Devolutions.RemoteDesktopManager.Managers.DevolutionsHubDataSourceManager.GetSystemTransactionStates(Guid dataSourceId)
at Devolutions.RemoteDesktopManager.Business.DataSources.HubSecuritySubDataSource.GetCacheID(CacheName cacheName)
Cross Vault Credential Usage
hi Stéfane,
Question, I tried to create another linked credential entry today using my workaround as mentioned above, but this time when I tried to pick a credential from my PAM Vault it didn't populate with entries like it had been, I also notice that the icon for the PAM Vault is a generic yellow folder icon when before it's a circular fav icons that you normally see for Vault names. Now nothing whatso ever has changed apart from regular updates, now I can't be sure If this is the first attempt at this workaround at my current version 2025.1.33.0 or whether it was 2025.1.33.0 when it was working or whether it worked in 2025.1.32.0 but isn't now??? I'm about to try in 2025.1.34.0, if there's any change Ill update this post but I'm not holding my breath as it may be an update with DPH bus that's patched my workaround?
How far off is your addition?
Thanks
Cross Vault Credential Usage
yeah that dph cred entry does the job, having my account settings set to the right entra user used for dph sso seems to prevent the extra steps to access the vaults, I like your form but would it look cleaner to have linked (vault) as it is now with the popup selector window with the tree view that defaults the current vault again, then add a vault selector drop down accross the top alongside the existing form fields where you see the vault search field with a 'name', 'tag' etc drop down field to its right, add a vault drop down there somewhere?? That way it should look much cleaner and users still have the expected linked (vault) which going by assumptions seemed like it should be doing what your changing now linking creds from vaults......
Cross Vault Credential Usage
Hi all,
I’m currently working on this feature and have just over three weeks to deliver it for inclusion in the 2025.1 release. At this time, it’s still too soon to say for certain whether I’ll be able to complete everything needed on time.
Reflecting on my earlier comment, it’s hard to believe this feature was first requested four years ago—how time flies! With the release of 2024.3, we made significant progress, including enabling background vault synchronization, which was a critical stepping stone toward cross-vault credential linking.
Currently, I’m focused on rewriting and validating the variable-resolving code. This is essential for allowing RDM to isolate each vault so that variables can be resolved independently, without cross-vault contamination. I’ll also need to apply the same changes across each subsystem in RDM (permissions, inheritance, etc.).
I’ll provide another update once the feature is released.
Best regards,
Hi Stéfane,
I was searching for cross vault linking in my case cross vault credential linking, then came accross this post, I see you were working on something for a 2025.1.x release, did it happen?? If so exaclty what was it, I see you mention variables but will your addition / change work for my scenario?? Granted I mainly use my personal vault or now PAM vaults for most credentials, but as you can tell I've come accross the need to use Credential entries from another vault but have been hitting a road block on how to proceed, I initially looked for an entry that could link cross vaults but couldnt find anything, then I started to look if Syncronizers could work, which then led me to consider just scripting this (This is similar to another problem ive not succeeded with which is propergation scripts for PAM vault creds). Anyway, would what your working on work for my scenario, has it released yet (soz yet to search through rls notes)
Scrap my previous I've just answered my own question DOH!!
This entry did the job...

Cross Vault Credential Usage
Hi all,
I’m currently working on this feature and have just over three weeks to deliver it for inclusion in the 2025.1 release. At this time, it’s still too soon to say for certain whether I’ll be able to complete everything needed on time.
Reflecting on my earlier comment, it’s hard to believe this feature was first requested four years ago—how time flies! With the release of 2024.3, we made significant progress, including enabling background vault synchronization, which was a critical stepping stone toward cross-vault credential linking.
Currently, I’m focused on rewriting and validating the variable-resolving code. This is essential for allowing RDM to isolate each vault so that variables can be resolved independently, without cross-vault contamination. I’ll also need to apply the same changes across each subsystem in RDM (permissions, inheritance, etc.).
I’ll provide another update once the feature is released.
Best regards,
Hi Stéfane,
I was searching for cross vault linking in my case cross vault credential linking, then came accross this post, I see you were working on something for a 2025.1.x release, did it happen?? If so exaclty what was it, I see you mention variables but will your addition / change work for my scenario?? Granted I mainly use my personal vault or now PAM vaults for most credentials, but as you can tell I've come accross the need to use Credential entries from another vault but have been hitting a road block on how to proceed, I initially looked for an entry that could link cross vaults but couldnt find anything, then I started to look if Syncronizers could work, which then led me to consider just scripting this (This is similar to another problem ive not succeeded with which is propergation scripts for PAM vault creds). Anyway, would what your working on work for my scenario, has it released yet (soz yet to search through rls notes)
[FEATURE REQUEST] Websites with Alternate credentials, plus ALTERNATE PROFILES?
Hi @john.kenny,
I'm Maxime, Team Lead on Hub at Devolutions.
I have a few questions for you to assist you better.
Are we discussing Hub Business or Hub Personal?
Is this issue specific to one entry, or do all your other entries get corrupted once updated?
Does this occur also with newly created entries, and then updating them causes corruption?
Are you able to restore 1 of your corrupted entry with RDM 2025.1.31.0 to a working version in RDM (View - Entry History)?
If yes, can you test out if you are able to update that entry using the Hub's web interface.
After your responses, we will try to reproduce the issue on our end, and if we cannot reproduce, we will ask you to open a support ticket with us.
Ok, looks like it's just one entry, which I've just realised so i've recreated it and now it's fine. Wonder how that happened?
Thanks anyway.
[FEATURE REQUEST] Websites with Alternate credentials, plus ALTERNATE PROFILES?
got another error today lol after updating to 2025.1.31.0 64bit, I can create new web entries but editing I get this notification but can't find it in activity logs?? I tested by creating a new entry which worked but editing and saving the edit I got the same notification on windows and the entry didn't save / update.
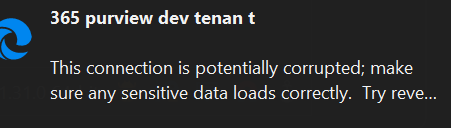
Ideas?
[FEATURE REQUEST] Websites with Alternate credentials, plus ALTERNATE PROFILES?
Hello John,
Good news, I believe we found what the "issue" is!
At the bottom right of your RDM window, in the status bar, there's an 'anchor' icon:
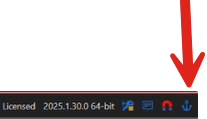
In your video we noticed it's checked. If you hover your mouse over it, you'll see the description of the setting: "Keep current focused content while opening a new tab".
You must have misclicked it at some point, but unchecking it should resolve this focus behavior.
Let me know if that worked!
Regards,
Doh, yep that was it!
You're an absolute star! Many thanks, I knew you guys would see what I'd missed lol
Thanks
[FEATURE REQUEST] Websites with Alternate credentials, plus ALTERNATE PROFILES?
You should see that the first entry opens and does focus, but not with the preceding entries
, they require tab clicks to focus manually? Quite some time ago RDM would focus on every new opened entry automatically yet I've obviously changed a setting that's preventing auto focusing now?
Thanks, fyi its a livable issue that I can cope with, its just something that's bugged me for ages now and I've finally got to the point i have to fix it. Ideally without factory resetting RDM settings....