
Craig Roser
2026.3.x ignoring roles assigned to "everyone" In devloutions server
and i just saw this on the notes in Server 2026.3.6.0, so i guess this is already fixed
Core - Fixed an issue where roles assigned to the "Everyone" user group were not applied to all users
2026.3.x ignoring roles assigned to "everyone" In devloutions server
We have a Vault logs viewer (Legacy) role for connection log viewer assigned to the everyone option. On connections view -> logs is now greyed out.
We use AD accounts, assigning the role to the AD groups in devolutions server makes it work. Confirmed by setting the role back to just everyone and its greyed out again.
Checked with the new built in role Workspace log viewer role as a test the same behaviour is observed.
Switched back to Vault logs viewer (Legacy) assigned it to every group listed, problem worked around.
It's ignoring roles assigned to everyone
Devolutions server 2026.3.5.0 using MSSQL
Duo Certificate Pinning
I have the same question as this https://forum.devolutions.net/topics/51915/duo-certificate-pinning but for server since if you're using web you don't need the RDM client.
Action Required by February 2, 2026: Announcing Duo certificate authority bundle expiration
Please ensure that you update all affected applications as well as the Duo Mobile application on phones.
Failure to update the affected applications and application versions described in this guide will impact user access and authentication!
This guide provides background information about Duo's root certificate authority (CA) bundle replacement and guidance for updating affected applications before February 2, 2026.
Is any update required?
Can't duplicate folders if no view password permissions
we're running devolutions server and users do not have the view password permissions. at some point with a client update they can no longer duplicate folders and get
The "View password" permission is required to perform this action.
This used to work in previous versions. currently running 2024.3.26.0
This seems to be an issue after a previous bug of the duplicate option just not showing up was fixed in Version 2024.3.18.0 (November 12, 2024)
Fixed duplicate action not being accessible in certain circumstances
We were indeed missing the duplicate action from the menus when we were running either 2024.3.13.0 or 2024.3.15.0 ( i can't remember which) it showed and worked fine up till then.
Disable Mouse Jiggler for all connections in Vault
Hi Friends,
I've updated devolutions server to 2023.3.12.0, however I'm having a little trouble finding where the setting is, I'm not sure what/where the type settings tab is. Any chance you could get a screenshot?
Disable Mouse Jiggler for all connections in Vault
I was using 2023.3.23.0 and 2023.3.24.0, while having it default to off in .25 is an improvement. For compliance we still need a way to ensure its off for all users and they can't turn it on.
Disable Mouse Jiggler for all connections in Vault
I've noticed on the other feature request for the jiggler you guys made a GPO for the RDM to disable, however not all our users are on the domain so we can't force policies on them.
Disable Mouse Jiggler for all connections in Vault
Is it possible to have the new RDP mouse Jiggler disabled (it looks like it defaults to default on) via a setting on devolutions server for everything in a vault.
It's a security issue allowing users RDP sessions to have a way of never disconnecting, especially when we've created policies on the server to discon/logout the users on inactivity. I've now got people staying connected to servers for hours after they've finshed because they simply just walk away from their PC leaving everything open.
(We also have applocker agents installed that stops non whitelisted apps, like jiggler apps)
Secret Server Searching
Nice, thanks guys just had this pop up again in a request.
Can confirm this works exactly how I wanted.
Cheers.
Auto update error message in RDM
hello i also just noticed this today as well, saying the new version is higher than maximal version on devolutions server when the maximal version isn't actually enabled on the server. I don't know if this will affect connection to the server as i've told people to hold off updating it.
EDIT: on the server ticking the maximal version box and changing the version to a higher version number (i set it to 2099.2.29.0) then unticking the maximal version box makes the message stop displaying. Looks like it doesn't care if the setting is enabled or not.

Secret Server Searching
with a secret server credential is there any way to search for a secret in a certain folder using the $COMPANY_NAME$ variable? All our secrets have the same name but are in \clients\clientname\ where clientname is the name of the client the secret is always called the same thing in that folder.
if i could do something like in the secret name box on this screenie \clients\$COMPANY_NAME$\Office 365
otherwise i need to go make a credential in rdm for every single client using the picker pointing specifically at their secret in secret server, which sounds like i'm going to have a bad day if thats the case.
an alternate feature would be being able to pick the secret by just typing the secret server ID number, the picker is super slow to use to have to click though all the screens.

Devolutions server 2021.2.8.0 Secret server Issues
Thank you! 2021.2.15.0 seems to have fixed it
Devolutions server 2021.2.8.0 Secret server Issues
Hello,
We just upgraded from server version 2021.1.17.0 to 2021.2.8.0 everything upgraded fine.
We're now seeing issues with Secret Server password types. In both the old client version 2021.1.20.0 and the new 2021.2.14.0.
The older client now just see's secret server passwords as a blank standard username / password secrets, it doesn't even fire the secretserver user / pass radius code prompt when used.
The new client shows them as secret server passwords. But when I try and use one I get the new duo code prompt, can see it logging in to secret server (with duo ok) on the secret server side. however it doesn't look like its parsing the list of secrets from the SS API output correctly. It's not showing all the folders from secret server, looks like its only showing the last subfolder(also has more subfolder in) of the first folder in secret server and then only 10 folders entries in those folders. Selecting one of the folders it does show then brings up an error 'sequence contains no matching element' and displays no secrets
Seeing as it worked ok before the devolutions server upgrade I think its a server issue with the new version?
Attached are some screenshots, I've included some of our secret server folders so you can see the missing folders that aren't showing. I've had to blank some things in the screenshots.


Weirdness with UI and VPN SSH with SSH shell connections
forgot to mention started noticing it on version 2021.1.32(could have been doing it before that but we didn't notice) updated to 2021.1.25 and it still has the issue
Weirdness with UI and VPN SSH with SSH shell connections
I have connections which work fine, if i edit them(or duplicate) they break and won't resave. namely because I have vpn/ssh/gateway SSH forwarding tunnels, it clears the destination field when you open it for editing. It also changes the vpn host field to whatever was originally set in the general -> hosts field (also the port number)
Oddly if i fix up the things and then you edit the general -> hosts field and then save it, that field reverts back to whatever it says in the vpn ssh hosts field (i'd usually have an external ip in the vpn hosts field(first screenshot) and localhost in the general hosts field(second screenshot) to use that ssh local forward tunnel).
Any thoughts on this?


Issues with Duo Security Push 2FA Since Upgrade
EDIT: nvm, found how to change
Thank you this resovles it
Issues with Duo Security Push 2FA Since Upgrade
Further testing, The below is all for the same user in order, users that i don't remove/re-add Duo, the use alternate button does nothing but make the duo box disappear then it just sits there.
Test1:
I clear 2fa off the user, save setting. Then set the 2fa duo back on for user to set up next login.
It allows them to set it up when they reopen RDM
then it does another push.
This time it works and logs in RDM that one time.
After closing and opening the RDM again it goes back to having the original problem.
Test2:
I clear 2fa off the user, save setting. Then set the 2fa duo back on for user, and send them a push which the user accepts
The user opens RDM
it does a duo push
the user click accept on their phone. This time it works and logs in RDM
User closes and opens RDM, duo push works as it should
User closes and opens RDM again, it goes back to having the original problem.
Test3:
User opens RDM as normal
it does the duo push
user accepts on their phone. Nothing happens in RDM (like they didn't click accept)
User Clicks Use Alternate, the window goes away and comes back and does another push
the user click accept on their phone. This time it works and logs in RDM
Issues with Duo Security Push 2FA Since Upgrade
Hello,
Yesterday we upgraded our server to 2021.1.7.0 so we could upgrade the manager to 2021.1.20.0 (which we have done as well)
Everything is working except 1 thing, all our users use Duo Security Push notification. Its sending the push but when you accept it on your phone nothing happens on the rd manager client. It just sits there like you haven't pressed accept. If you enter the passcode and press validate it works fine, so i have the users doing that so they can use it.
Users are AD based.
Oddly, if they try the web interface(which we don't use as connections through SSH tunnels don't work in it) the push works there ok. So I'm not sure if it's the server being the problem or the new version of RDM.
If you could let me know what to do next would be great.
Craig
SSH Gateway Multiple Outgoing tunnel settings
would it be possible to have multiple outgoing tunnels on this screen. For instance on this connection i would also like port 5900 forwarded as well as the 443 port. Basically I'm asking to have like the SSH Forward connection type but with the use dynamic port available, obviously one dynamic port per destination port. Would also like the $DYNAMIC_PORT$ variable able to populate with those multiple ports somehow be it $DYNAMIC_PORT1$ $DYNAMIC_PORT2$ or some other way.

Password server update 6.1.3.0 to 2019.1.14.0 - No 2FA settings any more
Hi Erica,
Appreciate the help on this but still having problems.
Tried to do the update again and it said it completed.
In testing both 14.1.3.0 & 2019.1.25.0 clients after user/pass duo accept the client now goes not responding. Eventually it comes back with the login to the repository screen again, then does the same thing if you try again.
I had to roll back again so people can use it.
No longer getting any error popups or error emails so I don't have anything else to report for you.
Password server update 6.1.3.0 to 2019.1.14.0 - No 2FA settings any more
Oh i see what you're asking, no i don't have the dps app there. I don't ever recall seeing it either is it new to the newer versions?
Password server update 6.1.3.0 to 2019.1.14.0 - No 2FA settings any more
Hi Erica,
I've run that sql query now, there was 1 null entry. Haven't tried the upgrade again yet.
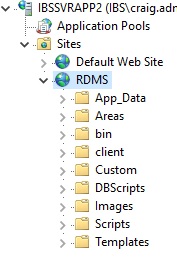
Website is in its own RDMS Site not Default Website (files are in c:\devolutionserver), in the bindings it is using a host header for the fqdn and only bound to 443. That could be a problem if its using something like a localhost call to the site?
Thanks,
Craig
Password server update 6.1.3.0 to 2019.1.14.0 - No 2FA settings any more
Hi Again,
I've tried going to 2019.1.17 still having issues although a different issue.
Now when a user goes to login it does all the duo stuff and they accept the push it says can not connect to datasource.
It also emails me the following errors, not sure what the difference as to each one i get.
I've had to roll it back again.
The bottom of the upgrade install says this the app pool is called RDMS
...
Upgrading database for data source 'Remote Desktop Management Server' with version 523
Done!
Restoring encryption file...Done!
Updating encryption file...Done!
Restoring the configuration...System.FormatException: The application pool name must be between 1 and 64 characters.
at Microsoft.Web.Administration.ApplicationPoolCollection.ValidateName(String name)
at Microsoft.Web.Administration.ApplicationPoolCollection.Add(String name)
at Devolutions.RemoteDesktopManager.Managers.IISManager.CreateEditApplicationPool(String applicationPoolName, String runtimeVersion, ManagedPipelineMode pipelineMode)
...Checking .NET Framework runtime
...Saving settings in database
...Saving connection string in web.config
...Saving Scheduler connection string
...Saving emails configuration in web.config
...Saving encryption configuration
...Done!
Restoring the custom folders...Done!
Install scheduler service...Done!
Starting scheduler service...Done!
Starting the web application...Done!
Upgrade to version 2019.1.17.0 completed!
The following error was received by tom at 8/07/2019 1:37:58 PM
Error:
ArgumentNullException - Value cannot be null. Parameter name: source at System.Linq.Enumerable.FirstOrDefault[TSource](IEnumerable`1 source, Func`2 predicate) at Devolutions.Server.ServerCacheManager.GetConnectionRoot(Guid repository) at Devolutions.Server.SecurityRoleManager.HasAccess(SessionContext context, Guid repositoryId, SecurityRoleDataSourceRight right) at Devolutions.Server.Controllers.APIControllers.V2.BackendApiController.GetLoginAccessEntity(SessionContext context) at Devolutions.Server.Controllers.APIControllers.V2.BackendApiController.DoLogin(SessionContext context, String userName, String password, ClientApplicationInfo clientApplicationInfo, String twoFactorID, TwoFactorInfo twoFactorInfo, String publicIPAddress, Byte[] sessionKey, String repositoryId, Boolean partialMode, Boolean useWindowsAuthentication, Boolean useAzureADAuthentication, String localMachineName, String localMachineUserName) at Devolutions.Server.Controllers.APIControllers.V2.BackendApiController.Login(LoginData loginData, Boolean partialMode) at lambda_method(Closure , Object , Object[] ) at System.Web.Http.Controllers.ReflectedHttpActionDescriptor.ActionExecutor.<>c__DisplayClass10.b__9(Object instance, Object[] methodParameters) at System.Web.Http.Controllers.ReflectedHttpActionDescriptor.ExecuteAsync(HttpControllerContext controllerContext, IDictionary`2 arguments, CancellationToken cancellationToken) --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Controllers.ApiControllerActionInvoker.d__0.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__0.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__0.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Controllers.ActionFilterResult.d__2.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Controllers.ExceptionFilterResult.d__0.MoveNext() --- Default
Source:
System.Core
The following error was received by brian at 8/07/2019 1:37:24 PM
Error:
InvalidOperationException - Nullable object must have a value. at System.ThrowHelper.ThrowInvalidOperationException(ExceptionResource resource) at Devolutions.Server.ServerCacheManager.<>c__DisplayClass58_0.b__2(ConnectionInfoEntity c) at System.Collections.Generic.List`1.ForEach(Action`1 action) at Devolutions.Server.ServerCacheManager.RefreshConnections(Byte[] clientVersion) at Devolutions.Server.Controllers.APIControllers.V2.BackendApiController.GetAllConnectionStates() at lambda_method(Closure , Object , Object[] ) at System.Web.Http.Controllers.ReflectedHttpActionDescriptor.ActionExecutor.<>c__DisplayClass10.b__9(Object instance, Object[] methodParameters) at System.Web.Http.Controllers.ReflectedHttpActionDescriptor.ExecuteAsync(HttpControllerContext controllerContext, IDictionary`2 arguments, CancellationToken cancellationToken) --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Controllers.ApiControllerActionInvoker.d__0.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__0.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Web.Http.Filters.ActionFilterAttribute.d__5.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.ActionFilterAttribute.d__0.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Controllers.ActionFilterResult.d__2.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Filters.AuthorizationFilterAttribute.d__2.MoveNext() --- End of stack trace from previous location where exception was thrown --- at System.Runtime.ExceptionServices.ExceptionDispatchInfo.Throw() at System.Runtime.CompilerServices.TaskAwaiter.HandleNonSuccessAndDebuggerNotification(Task task) at System.Web.Http.Controllers.ExceptionFilterResult.d__0.MoveNext() --- Default
Source:
mscorlib
Password server update 6.1.3.0 to 2019.1.14.0 - No 2FA settings any more
Hi Folks,
Any news on this one?
Craig
Password server update 6.1.3.0 to 2019.1.14.0 - No 2FA settings any more
2FA usage is set to Required.
Noted about the database, only didn't restore it as a test. Have restored it now.