
daniilbarabasev
MFA caching for PSM SSH Proxy not working
Hello Patrick,
The PVWA/CPM address is correct, as I set up this CyberArk instance specifically to test MFA caching with RDM. However, you might be right about the certificate chain or some misconfiguration on my side, so I moved to the second environment, where I'm confident the trust and connections are set up correctly. The downside is that I'm limited on how much I can change on the CyberArk side.
After some additional troubleshooting, I found a few things that were causing issues.
For a connection through PSMP, we normally use a string like:
ssh -i key.file primaryAccount@domain@targetAccount#domain@targetServer@proxyServer
To make this work, I had to configure the CyberArk PSM SSH Proxy entry as follows:
Set the username to primaryAccount@domain
Enable "Use MFA Caching" and fill out the configuration as documented
I had originally assumed that the username would not need to be provided, since it should be available from the SAML connection. That assumption was wrong.
Then in the SSH Shell entry:
Set the host to targetServer
Set the username to targetAccount#domain (if the target account is local, just use targetAccount)
Set VPN/Tunnel/Gateway to the configured CyberArk PSM SSH Proxy entry
With this setup, MFA caching works correctly. On the first connection, RDM prompts for SAML logon, and after that the SSH connection goes through seamlessly.
One additional issue I encountered:
Credential saved in the User Vault as "Primary Account login":
Username: username
Domain: domain
Password: ****
Then in the PSM SSH Proxy entry:
Credentials: Find by name (User Vault) > "Primary Account login"
Advanced > Username format: {User}@{Domain}
What I would expect with this configuration is that the resulting string matches the format above. However, after examining the logs, the domain is not included. The resulting string looks like primaryAccount@targetAccount... instead of primaryAccount@domain@targetAccount....
Fortunately, this is not a dealbreaker, as it can be worked around by extending the username in the credential entry to username@domain. With that change, the string is constructed correctly. This is workable for now and doesn't crash the application.
I'll test this in one more environment that uses RADIUS authentication instead of SAML, to confirm the settings are correct. I don't have direct access to that environment and will need to coordinate with a colleague, so my next response may be slightly delayed.
Thanks,
Daniil
MFA caching for PSM SSH Proxy not working
Hello Patrick,
I'm currently using RDM version 2026.2.7.0 (64-bit). As for the requests:
Environment 1:
The first error message is just this window:
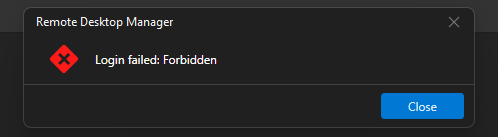
Then it disconnects me from the workspace and I have to log in again. Pressing Yes/No yields the same outcome:
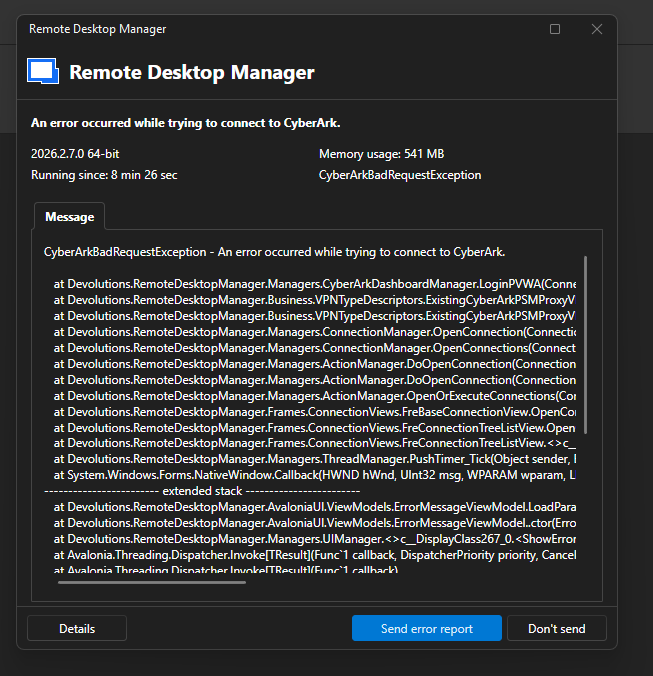
I've attached RemoteDesktopManager.log, RemoteDesktopManager.log.db, RemoteDesktopManager.debug, and the error message. If needed, I can attach more logs or increase the debug level. Please provide instructions on obtaining them.
The connection was tested and the error reproduced on 5 June 2026, around 14:00+ CET. One thing I noticed is that the log complained about an untrusted web certificate, so as a test I added it to the trusted root store, but the result was the same.
Environment 2:
After updating to version 2026.2.7.0, I'm unable to replicate the original issue. It now behaves the same as Environment 1. I'll keep you posted if anything changes.
The suggested workaround wouldn't work for us, as that is a different type of connection. It's not possible to launch a PSM SSH Proxy connection from the Dashboard/PVWA.
Best regards,
Daniil
CyberArk PSM connection workflow clarification
Hello William,
Thank you, this all makes sense. We'll move to the Dashboard + standard RDP entry approach. After testing, the PVWA credential entries seem to cover the per-server account workflow, I'll add to this conversation if I find anything else.
One thing remains. Using the Dashboard or a PVWA credential entry for the RDP launch works fine, but the credential source on the PVWA credential entry itself is an issue: there doesn't appear to be an option to pull credentials from the User Vault.
For context, our setup is several separate CyberArk environments, each with its own predefined PVWA connection, and multiple users sharing the data vault. Against that, none of the available credential sources fit:
- Custom (hardcoded into the entry): not suitable, since the vaults are shared.
- CyberArk AAM: not usable, we don't use AAM in any of our environments.
- My Account Settings (PVWA): not workable either, as it only holds a single account and can't distinguish between Dashboards. For example test and prod environments could use different accounts, so one per-user PVWA account can't cover both.
What we'd want is the ability to extend the ability to select credentials from the User Vault on the PVWA credential entry so it's more on pair with a selection in plain RDP (Find by name, Linked and so on). Is this already planned on your side, or should I raise a feature request for it? It would be nice to have these options added to all CyberArk related connection entries.
Thanks again,
Daniil
MFA caching for PSM SSH Proxy not working
Hello,
I've tried to set up two different PSM SSH Proxy connections with MFA Caching and neither of which succeeded
Environment 1:
The connection through the PSM SSH Proxy works, when the credentials are defined in the PSM SSH Proxy entry. However, if the MFA caching is enabled, the connection crashes.
The authentication mode is set to CyberArk and the credentials are hard coded into the entry:
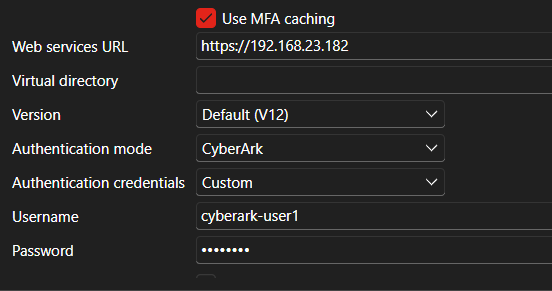
If I try to connect with this setting, I get two errors:
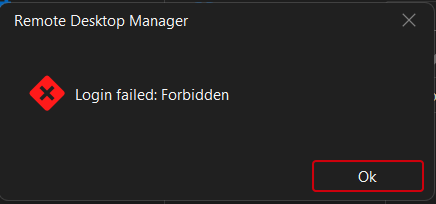
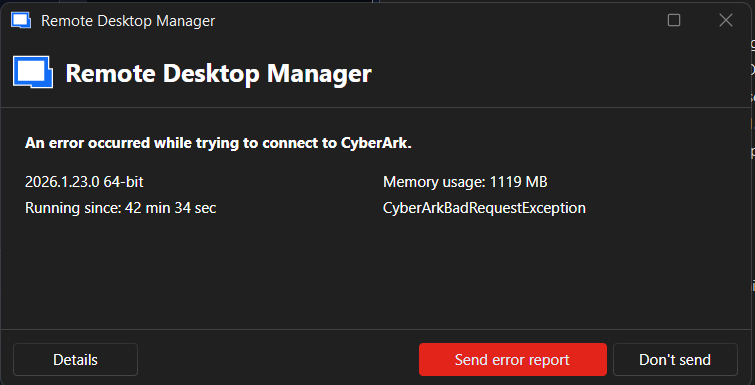
The SSH Terminal entry should be configured correctly, because it works without MFA Caching.
This is the latest CyberArk version (15.0), so I suspect the issue is caused by some change to the API. The passphrase for the key is not enabled.
Environment 2:
In this case, the CyberArk environment is on version 14.2 and there is enforced MFA with SAML, so the PSM SSH entry is configured for SAML authentication.
When trying to connect through the PSM SSH Proxy, it first asks for SAML authentication, which goes through correctly, but after that I get a prompt for interactive authentication:
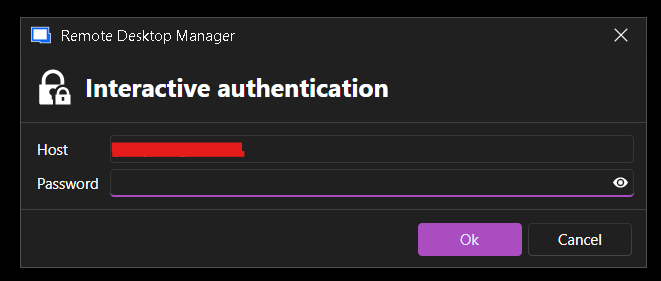
I have no idea which password it requests. The host field contains the hostname of the PSM SSH Proxy. In this case, the passphrase for the SSH key is enforced.
Could you confirm whether this is a known issue with the latest CyberArk versions, or whether there's a configuration on the RDM side I might be missing? I'm happy to provide logs, screenshots, or additional details from either environment if that would help with troubleshooting.
Thank you for your time.
Best regards, Daniil
CyberArk PSM connection workflow clarification
Hello,
I would like to confirm whether my understanding of the CyberArk PSM workflow in RDM is correct, and to raise a feature request based on a limitation we are hitting with multiple CyberArk environments.
My current understanding of the setup
1. Create a CyberArk Dashboard entry.
2. Create a CyberArk PSM Server entry (defining the PSM host and the authentication used to connect to the PSM server itself).
3. Create a CyberArk PSM Connection entry that references the PSM Server entry and specifies the privileged account and connection component.
My current understanding of how to launch a connection
1. Log in to the CyberArk Dashboard.
2. Open a safe that contains the account/entry I want to reach.
3. Right-click the PSM Connection entry and choose "Connect Using" and the previously defined CyberArk PSM Server.
Questions
1. Is this the correct/intended way to open connections through a PSM proxy using the PSM Server + PSM Connection entry types?
2. If I am not logged in to the CyberArk Dashboard, the "Connect Using" option does not appear on the PSM Connection entry. Is this intended, even though the PSM Server entry itself can hold a username/password (Custom mode)? If so, what is the intended purpose of those credentials stored on the PSM Server entry and when are they actually used versus the Dashboard session?
---
Fortunately, we can work around this with a plain RDP entry> connecting directly to the PSM server and specifying the program to run on connection as psm /u <user>@<address> /a <address> /c PSM-RDP. However, this wouldn't scale if we had multiple SAML-authenticated CyberArk environments that need to be defined through the Dashboard entry.
Thanks!
Kind regards,
Daniil