
lupowolfi
u2f security key support for Keeper integration
Thank you very much for your quick help Jonathan.
It's really refreshing to experience such dedicated support.
Much appreciated!
u2f security key support for Keeper integration
Login type: Vault login
Cache mode: disabled (would like be able to set it to 15min,30min,1hour, etc.)
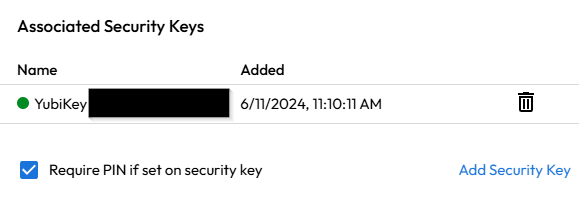
I readded the YubiKey but it did not change the behavior (previously I added it in nov 2024).
Additionally I also have a PIN requirement set.
u2f security key support for Keeper integration
Thanks for your quick reply.
I am using a Yubico YubiKey 5 NFC.
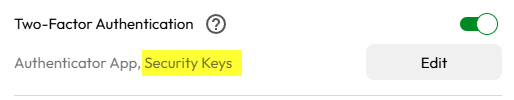
Yes, it is setup as second factor in Keeper as shown on your screenshot.
u2f security key support for Keeper integration
Hi,
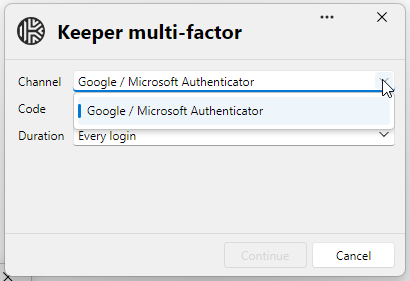
I updated to version 2026.3.8.0, but it seems for me the new feature seems not to work:
Kind regards
u2f security key support for Keeper integration
Hi Jonathan,
thank you very much for your efforts and for taking our feedback into account!
May I kindly ask whether this specifically refers to signing in with a FIDO2 security key as a second factor, or whether passwordless sign-in via WebAuthn is also supported?
Feature Request: More Flexible TOTP Authentication Caching for Keeper Integration
And yes for the YubiKey support we should keep the discussion in the other thread to avoid too much noise: https://forum.devolutions.net/topics/39333/u2f-security-key-support-for-keeper-integration
Spoiler - I just implemented it locally and it works
These are amazing news.
Alright, I'll keep that in mind and continue the YubiKey discussion there.
Thank you for your efforts!
Feature Request: More Flexible TOTP Authentication Caching for Keeper Integration
We are using username/password login, since we would like to keep Keeper separated from our current identity provider.
But if this point comes up, I would also like to add the following suggestion (although it would probably be better submitted as a separate feature request):
It would be great if authentication with Keeper could additionally be implemented using a passkey (WebAuthn), specifically with FIDO2 security keys such as a YubiKey.
To achieve a true passwordless login experience.
Keeper already supports this type of login in general.
Whether it would technically work with the RDM integration, however, I honestly do not know.
Feature Request: More Flexible TOTP Authentication Caching for Keeper Integration
Hi Jonathan,
thanks for the quick reply.
If there is no other way, this would already be an improvement!
But isn't there a way to issue something like a 12-hour session and then invalidate the cached credential/session earlier from the RDM side if needed? I'm also thinking about the other proposal I mentioned: requiring an MFA re-authentication after a screen lock.
u2f security key support for Keeper integration
Hi Hubert,
I am checking back in for this request.
How is the status?
Thanks
Feature Request: More Flexible TOTP Authentication Caching for Keeper Integration
Hello Devolutions Team,
We are using the Keeper Password Manager integration in Remote Desktop Manager (RDM) to manage and inject our credentials. Overall, the integration works quite well and we are happy with it.
However, we would like to suggest an improvement to make the user experience more practical and efficient.
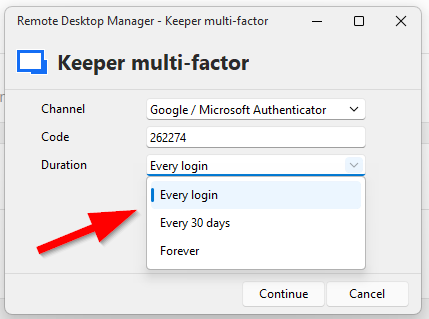
Currently, whenever we open an RDM connection entry that requires credentials from Keeper, we are prompted to enter a TOTP code. Even though the prompt provides options to adjust the authentication validity period, RDM still requires a new TOTP verification for every newly opened connection. That is, the provided option do no have any effect.
For administrators and support engineers who often open multiple connections within a short period of time, this becomes quite cumbersome. In practice, we sometimes have to wait for the next TOTP code to be generated before we can continue our work, which slows down workflows considerably.
We would therefore like request a fix of the problem and the ability to configure more practical authentication cache durations for the Keeper integration, for example:
30 minutes
1 hour
Custom time period
This would provide a better balance between security and usability for environments where multiple connections are opened consecutively.
We completely agree that periodic re-authentication with a second factor is important and should remain part of the security model. One possible approach could be to require re-authentication after the configured time period expires, or alternatively after the workstation has been locked and unlocked again.
We would appreciate any consideration of this request, or recommendations for alternative ways to improve the usability of the current Keeper integration.
Thank you for your excellent product and for continuously improving Remote Desktop Manager.
Best regards
Open new windows/pop-ups on monitor with main window
Thank you very much for the update and for considering my request.
Looking forward to see this implemented.
Open new windows/pop-ups on monitor with main window
Hi Hubert,
thank your for your quick response.
This is the first thing I tried, but at least for me it does not seem to work.
The application restart does not help.
I am on version 2026.1.19.0.
Open new windows/pop-ups on monitor with main window
I would like to ask whether it would be possible to implement a feature that ensures all newly opened RDM windows or pop-ups open on the same screen as the main window.
Would be great to have a option which enables this behaviour.
At the moment, new windows open on whichever monitor the mouse cursor is on.
Activity logs - Showing wrong "Active time"
Hi,
after upgrading to version 2026.1.11.0 of Remote Desktop Manager the issue seems to be fixed!
Thank you very much!
Kind regards
Activity logs - Showing wrong "Active time"
Hi Maxim,
thank you very much for your efforts.
Unfortunately, the issue seems to persist - at least in our environment.
I already responded to the ticket in question and attached a video that showcases the behaviour.
Feel free to reach out to me, if you need any details.
Kind regards
Activity logs - Showing wrong "Active time"
Thanks, I appreciate your efforts!
Looking forward to see this fixed.
Activity logs - Showing wrong "Active time"
Hi,
I noticed that the Activity Logs feature does not display the correct Active time. Instead, it shows the same value as the Duration field, which is obviously incorrect.
I have already opened a support ticket regarding this issue (ticket 00107199).
I hope this issue will be addressed soon, as we plan to integrate this feature into our time‑tracking system.
May I kindly ask if there is an ETA for addressing this issue?
Thanks!
Kind regards
u2f security key support for Keeper integration
Hi,
I’m wondering where things stand with this feature request - are there any updates?
Thanks!