
nciucci
Adoption of Delinea Platform authentication flow
For a testing thing, with the portable latest one, pointing to a Datasource in 2026.2.20 was working fine
Adoption of Delinea Platform authentication flow
Hi Niko,
Yes, you are facing the same issue.
In older versions of RDM, the SSO login process would fail to detect the session token and the embedded browser would remain open.
In a normal workflow, the embedded browser closes and RDM can then proceed with account retrieval.
I just checked, and RDM 2026.3.15 or newer should have the fix that allows the SSO flow to identify the token and correctly finish the login process.
Regards
@Jonathan Lafontaine
Thank you so much for your quick answer!
This can be tested with the portable version of latest RDM pointing to DVLS 2026.2.20 or will not work for testing and i need to update all my infra?
Best regards
Niko
Adoption of Delinea Platform authentication flow
Hello @Dylan Ferris
I'm trying to setup as well Delinea Platform integration with Devolutions RDM. Not sure if this is the correct place.
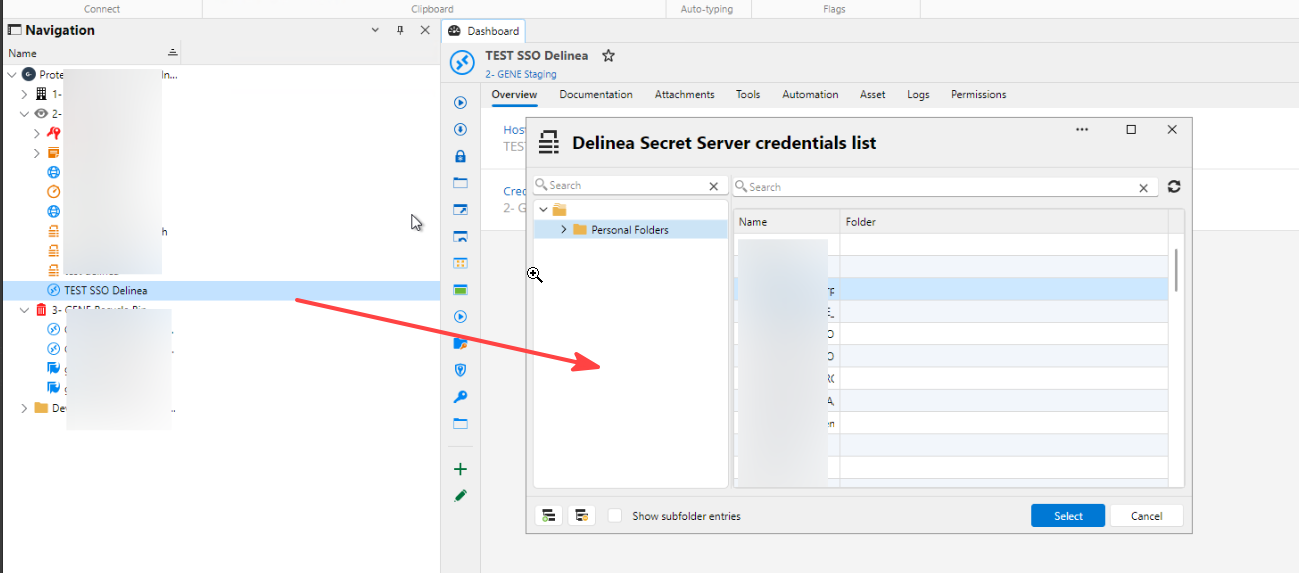
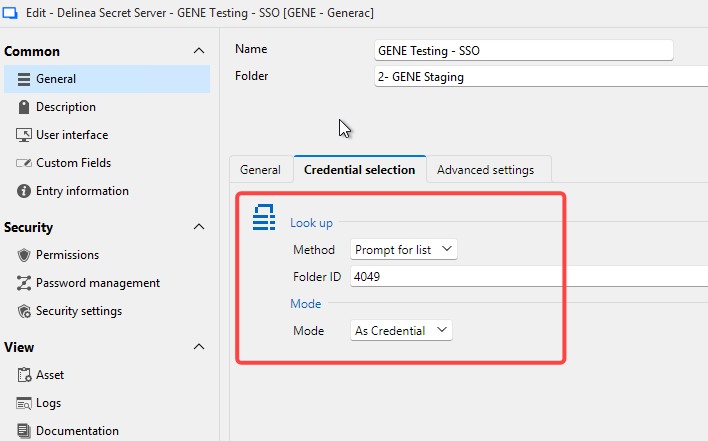
I was able to do SSO to Delinea Platform via Delinea Secret Server entry, with OTP and able to see the secret vault of Delinea, but not able to do "Method" -> "Prompt for list" in order to select, inject and open any connection entry like RDP/SSH for example.
We are talking of something that could be related?
I attached the entry of Delinea to an RDP, with the setting prompt for list
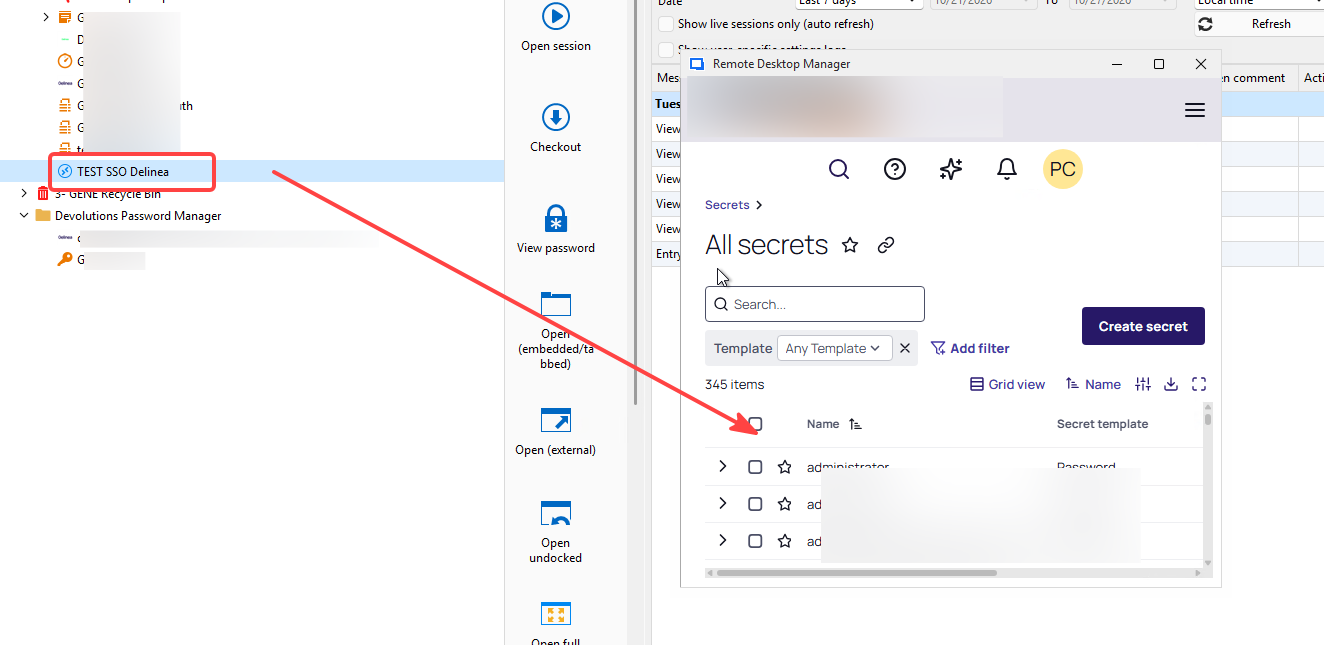
and is ending here, with nothing to inject:
Thanks in advance
DVLS v2026.2.20.2
RDM v2026.2.20.0
Niko
Enable Back in RDM $HOST$ as variable to Advance Multivault Search
Hello,
I'm running on version 2026.1.24 in RDM, and I'm not able to add the variable of "Advance Search -> Multivault -> by $HOST$.
On previous version that was available and very useful if you don't have the IP on the name structure of the entry, or similar.
Now if i have all my entries with IP in $HOST$ i can not search it.
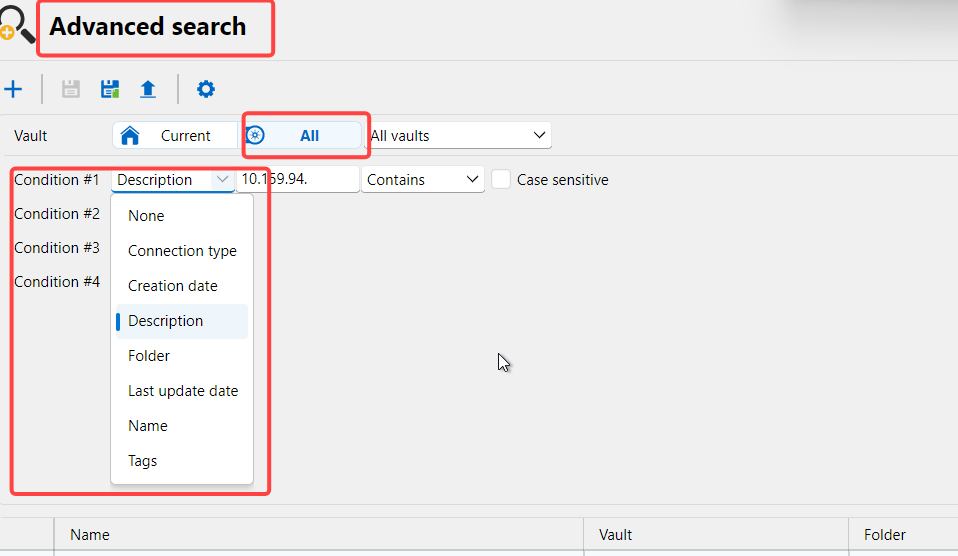
I open a chat with support and they confirmed that is not present on the next extended or the latest.
Please let me know
Thanks in advance
Nicolas
Add a way to view User Vault connection logs
Hello, we are enabling the User Vault in our DVLS environment, and i found that there is no way to see to which systems the users are connecting to from there in the console.
So my request is to have a way to, lets say "Administrators" in DVLS, to view in the Activity Logs the user vault logs of connections only at least.
If we can not do that we are losing the audit part with our customers to where and whom was connecting to their systems.
Also if you can select which kind of entries they can create on the user vault, lets say only credentials, that will be solved in our case.
Both options are good to have the audit on what they can do from there.
Please let me know if I was clear.
Best regards
Nicolas
RDM v2024.1.20.0 64b Issues with "Security Setting - Temporary Access"
I have another request for you as well, i dont know if you are looking to go to something more similar to the ADUC console in the Active Directory entry new, which is a great approach to grant this access to multiple domains for helpdesk management, but for onboarding tasks is a little complicated to use, for example to add extra attributes as "Managers" or "JobTitle", also to add multiple Security Groups per user. Those are in the scope as well?
RDM v2024.1.20.0 64b Issues with "Security Setting - Temporary Access"
Maybe is mine also, 2 months ago?
RDM v2024.1.20.0 64b Issues with "Security Setting - Temporary Access"
Hello Devolutions RDM Support,
I was facing this bug or issue on the application, when i set the Security Settings in an entry -> Temporary Access -> Mode -> Allowed -> Authorizers -> Custom, and then select an AD Group as Type, I'm not receiving the request, only the message. Now if i add an AD User as Type(direct users), I'm receiving the request, and the message with the correct notification on the Dashboard.
That is something in scope to be fixed or working?
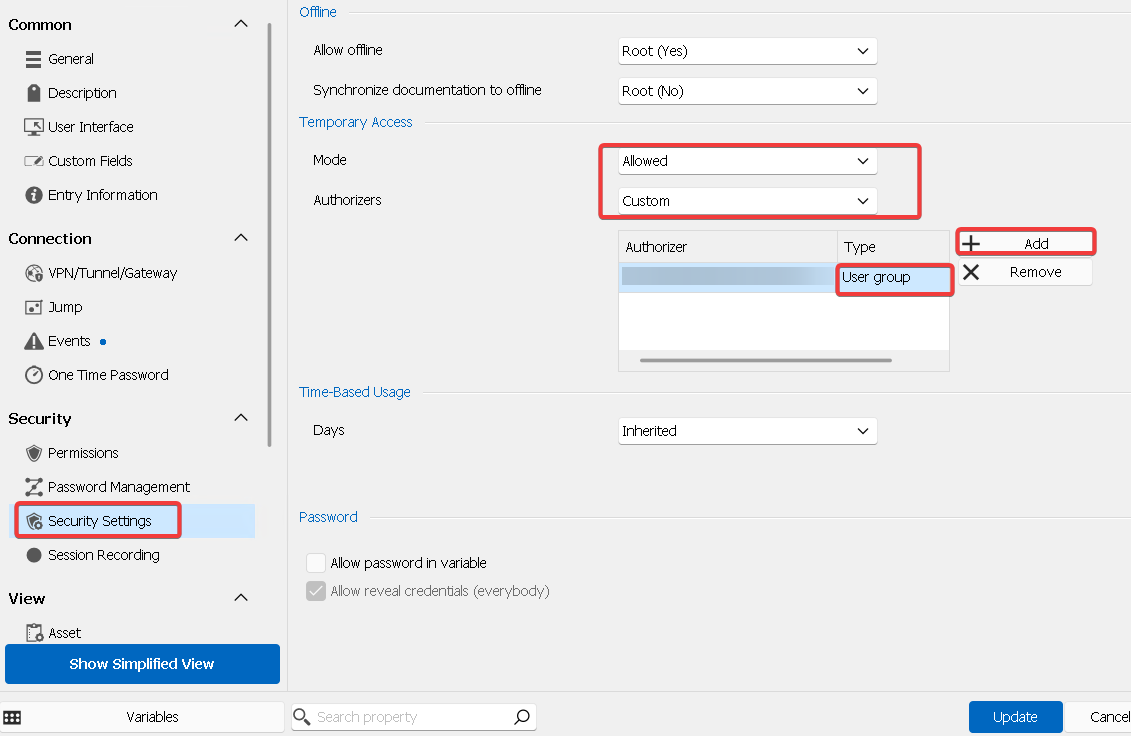
Thanks in advance
Best regards
Nicolas