
pengyi
Delinea Secret Server Integration with RDM and AAD IDP
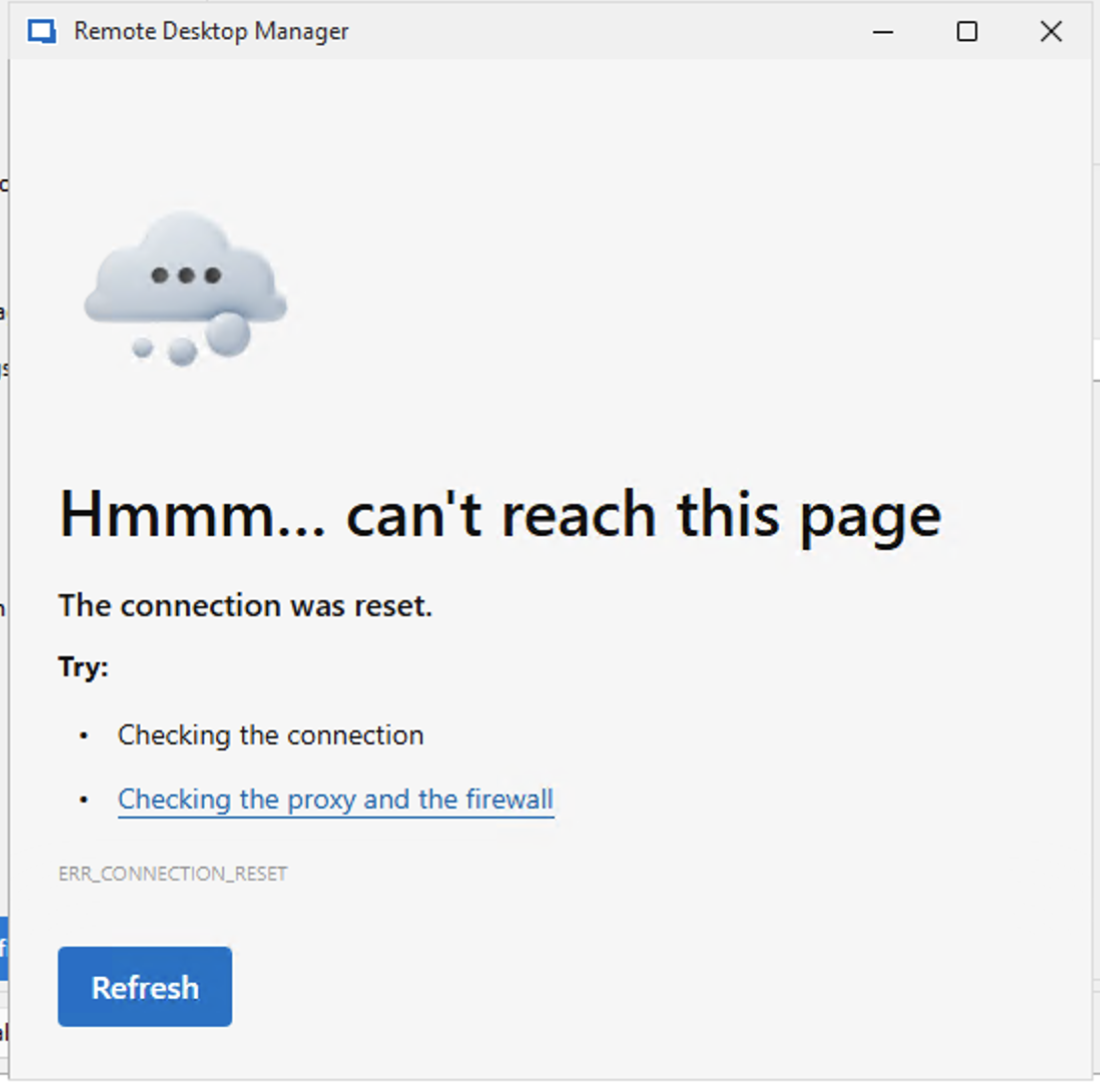
From the RDM's integrated browser, we tried to follow your video instruction, same "the connection was reset" error when using quick connect to the Delinea Secret Server landing page.
Thank you!
Delinea Secret Server Integration with RDM and AAD IDP
Hi Xavier,
Thank you for your reply!
Yes, we are able to connect to the Delinea Secret Server instance through an external browser from the same client.
Here is the application log error.
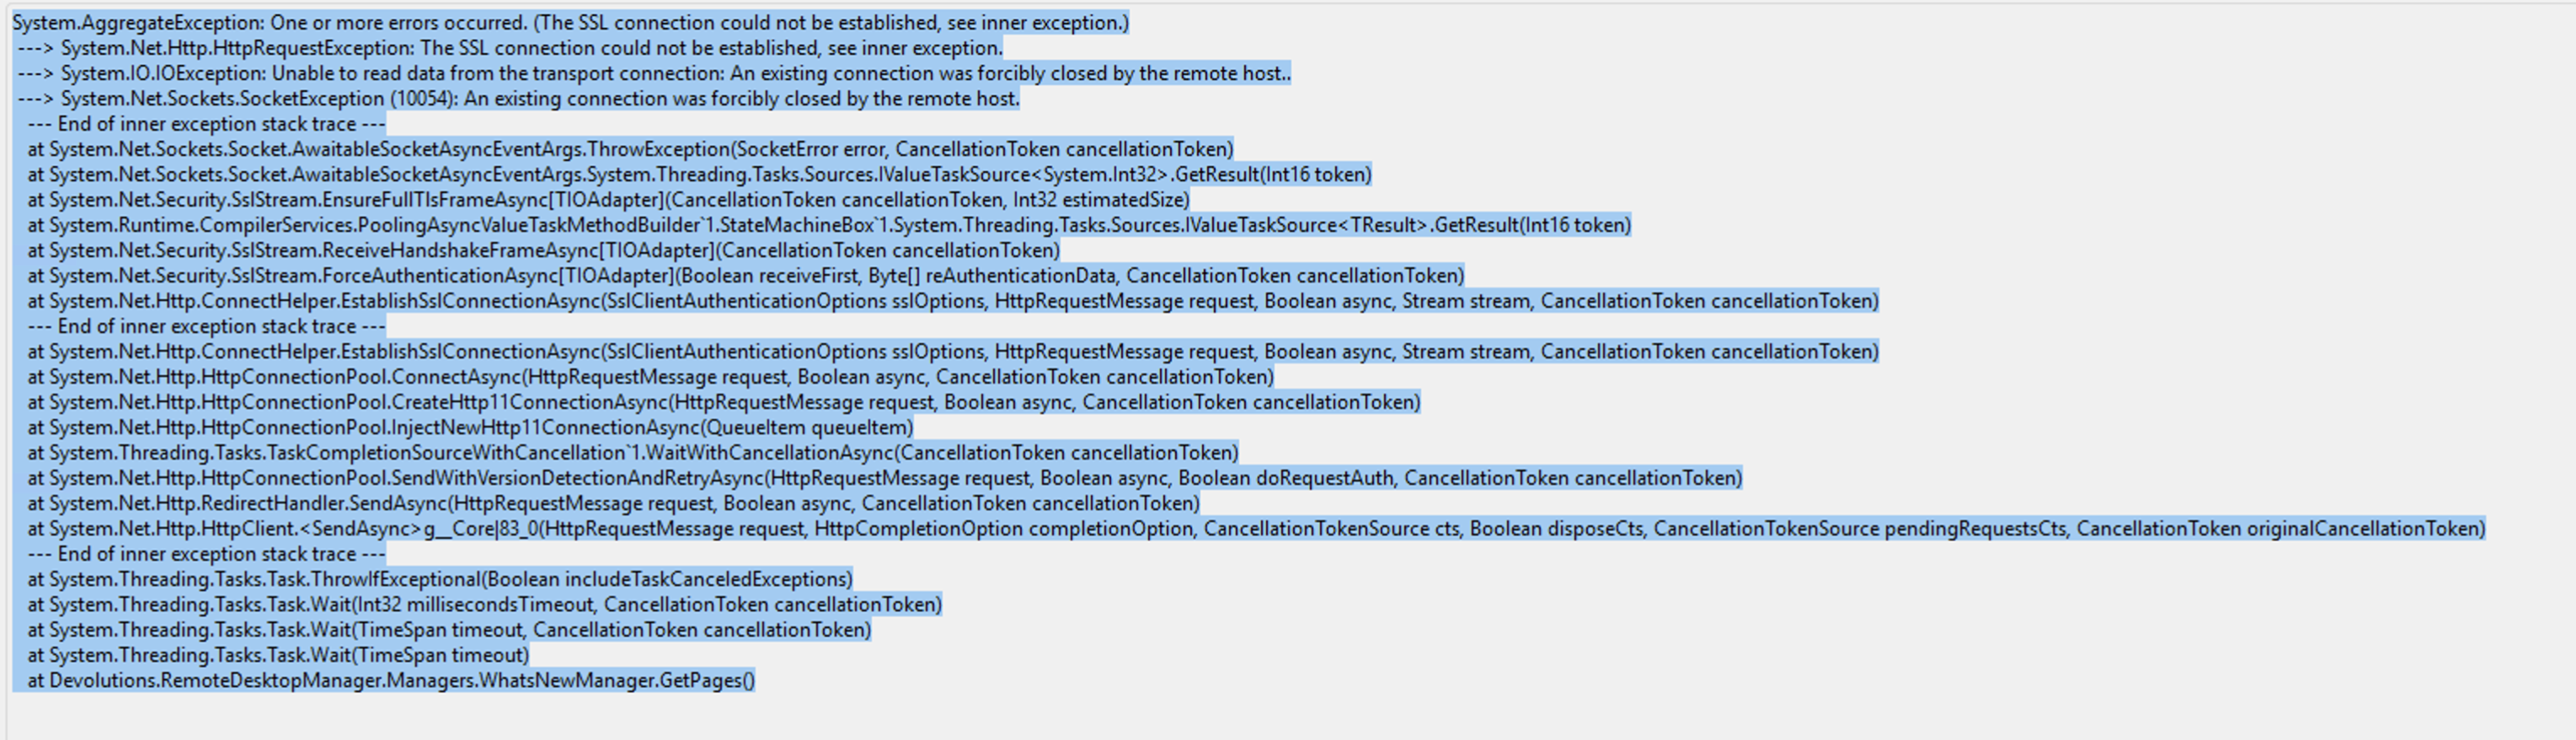
Let me check with the network team again to see if the proxy is modifying the request.
Delinea Secret Server Integration with RDM and AAD IDP
Hi Xavier,
Thank you very much for your suggestions.
We investigated internally but were still unable to identify the root cause.
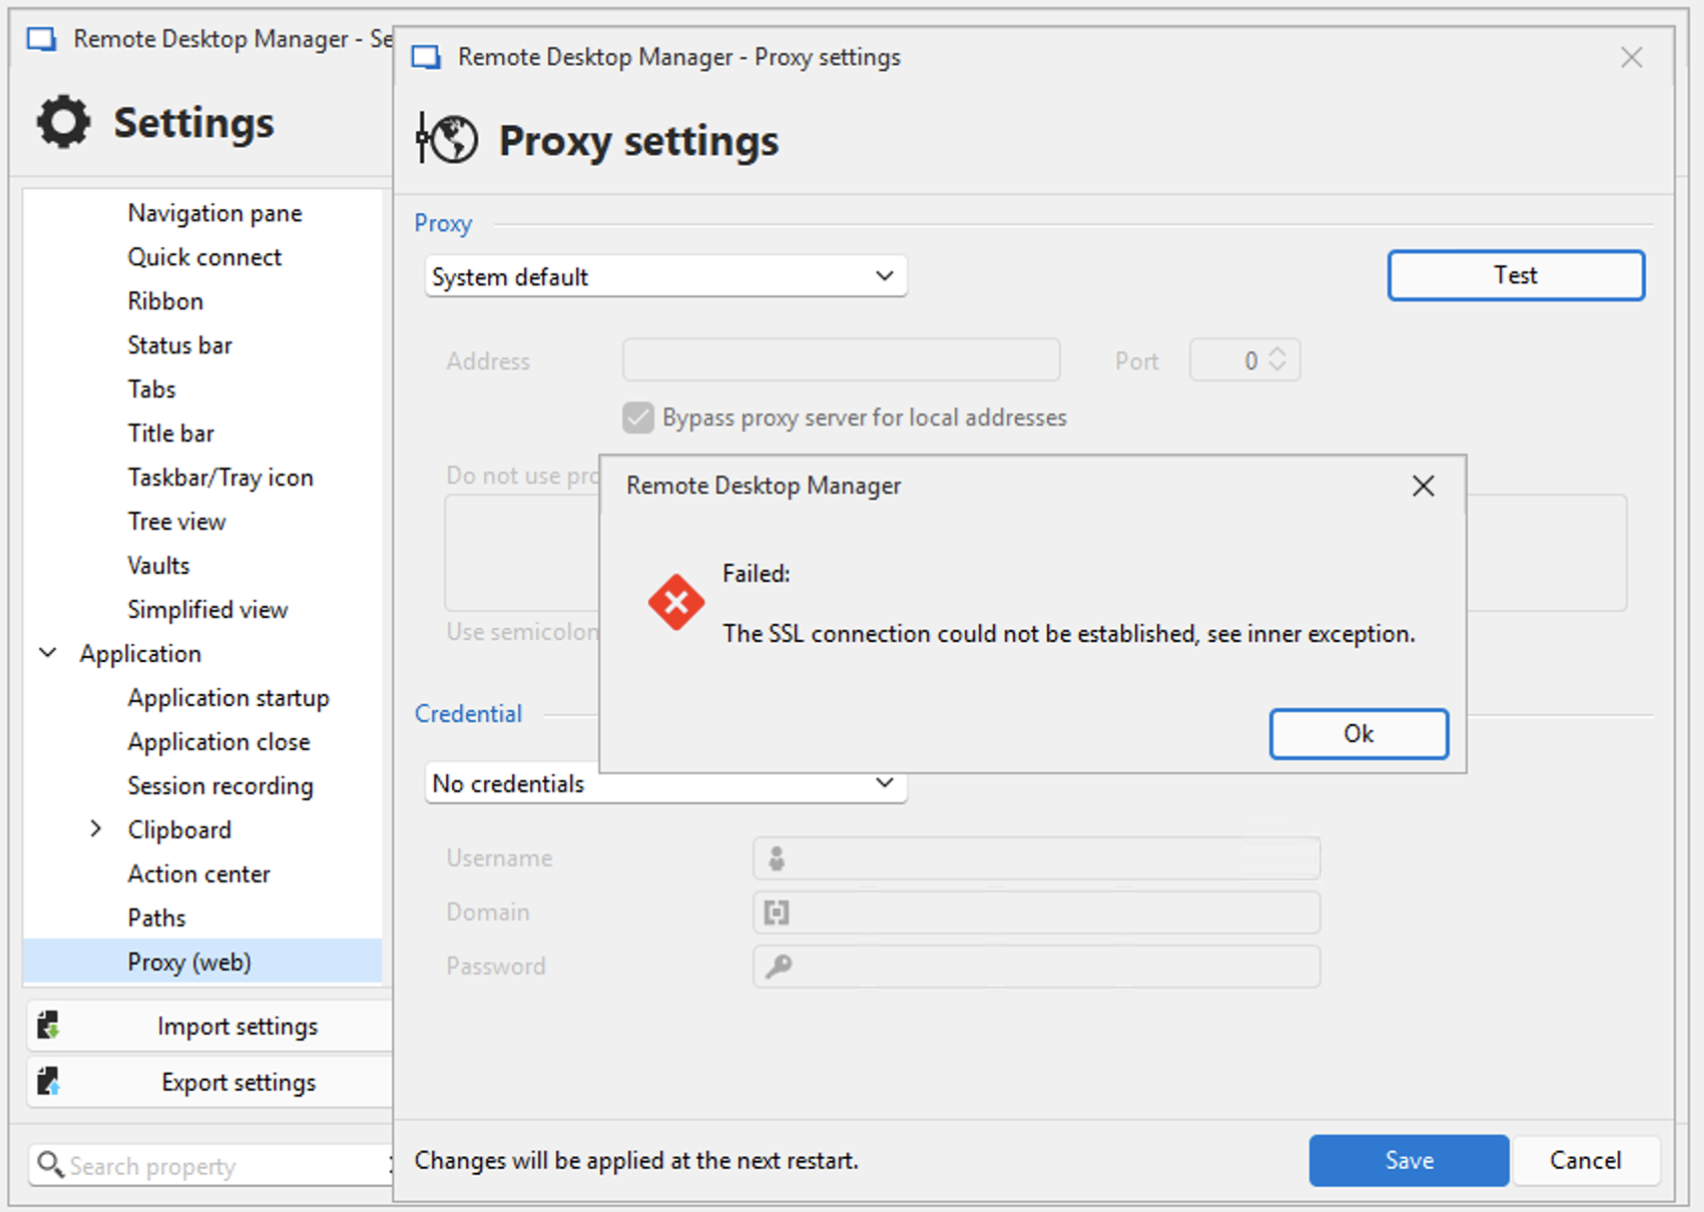
When we use the system’s default proxy and click the test button, we encounter the following error: “SSL connection could not be established.”
Do you have any idea what might be causing this?
On the other hand our network team checked and said the F5 is seeing a TLS 1.0 request from the client. My question is: How can I force Devolutions RDM to use TLS 1.2 instead of TLS 1.0 when opening a WebSession? Maybe this is the reason? When accessed the Secret Server web through the browser, the connection uses TLS 1.2, which functions properly.
Any help would be appreciated!
Delinea Secret Server Integration with RDM and AAD IDP
Thank you Xavier for your valuable advice!
Following your suggestion, we focused on the SSO authentication settings and discovered that something on the device is blocking RDM from successfully communicating the Delinea Secret Server.
Is there a way or any logs we can check to verify that in RDM?
Best Regards,
Peng
Delinea Secret Server Integration with RDM and AAD IDP
Hi All,
Not sure if anyone know if this setup works with the RDM integration.
On-Prem Delinea Secret Server installation
Secret Server Integration with multi AAD tenants for user sync https://docs.delinea.com/online-help/secret-server/directory-services/azure-active-directory/index.htm
enforced AAD MFA policy
RDM integration works well with on-prem AD users
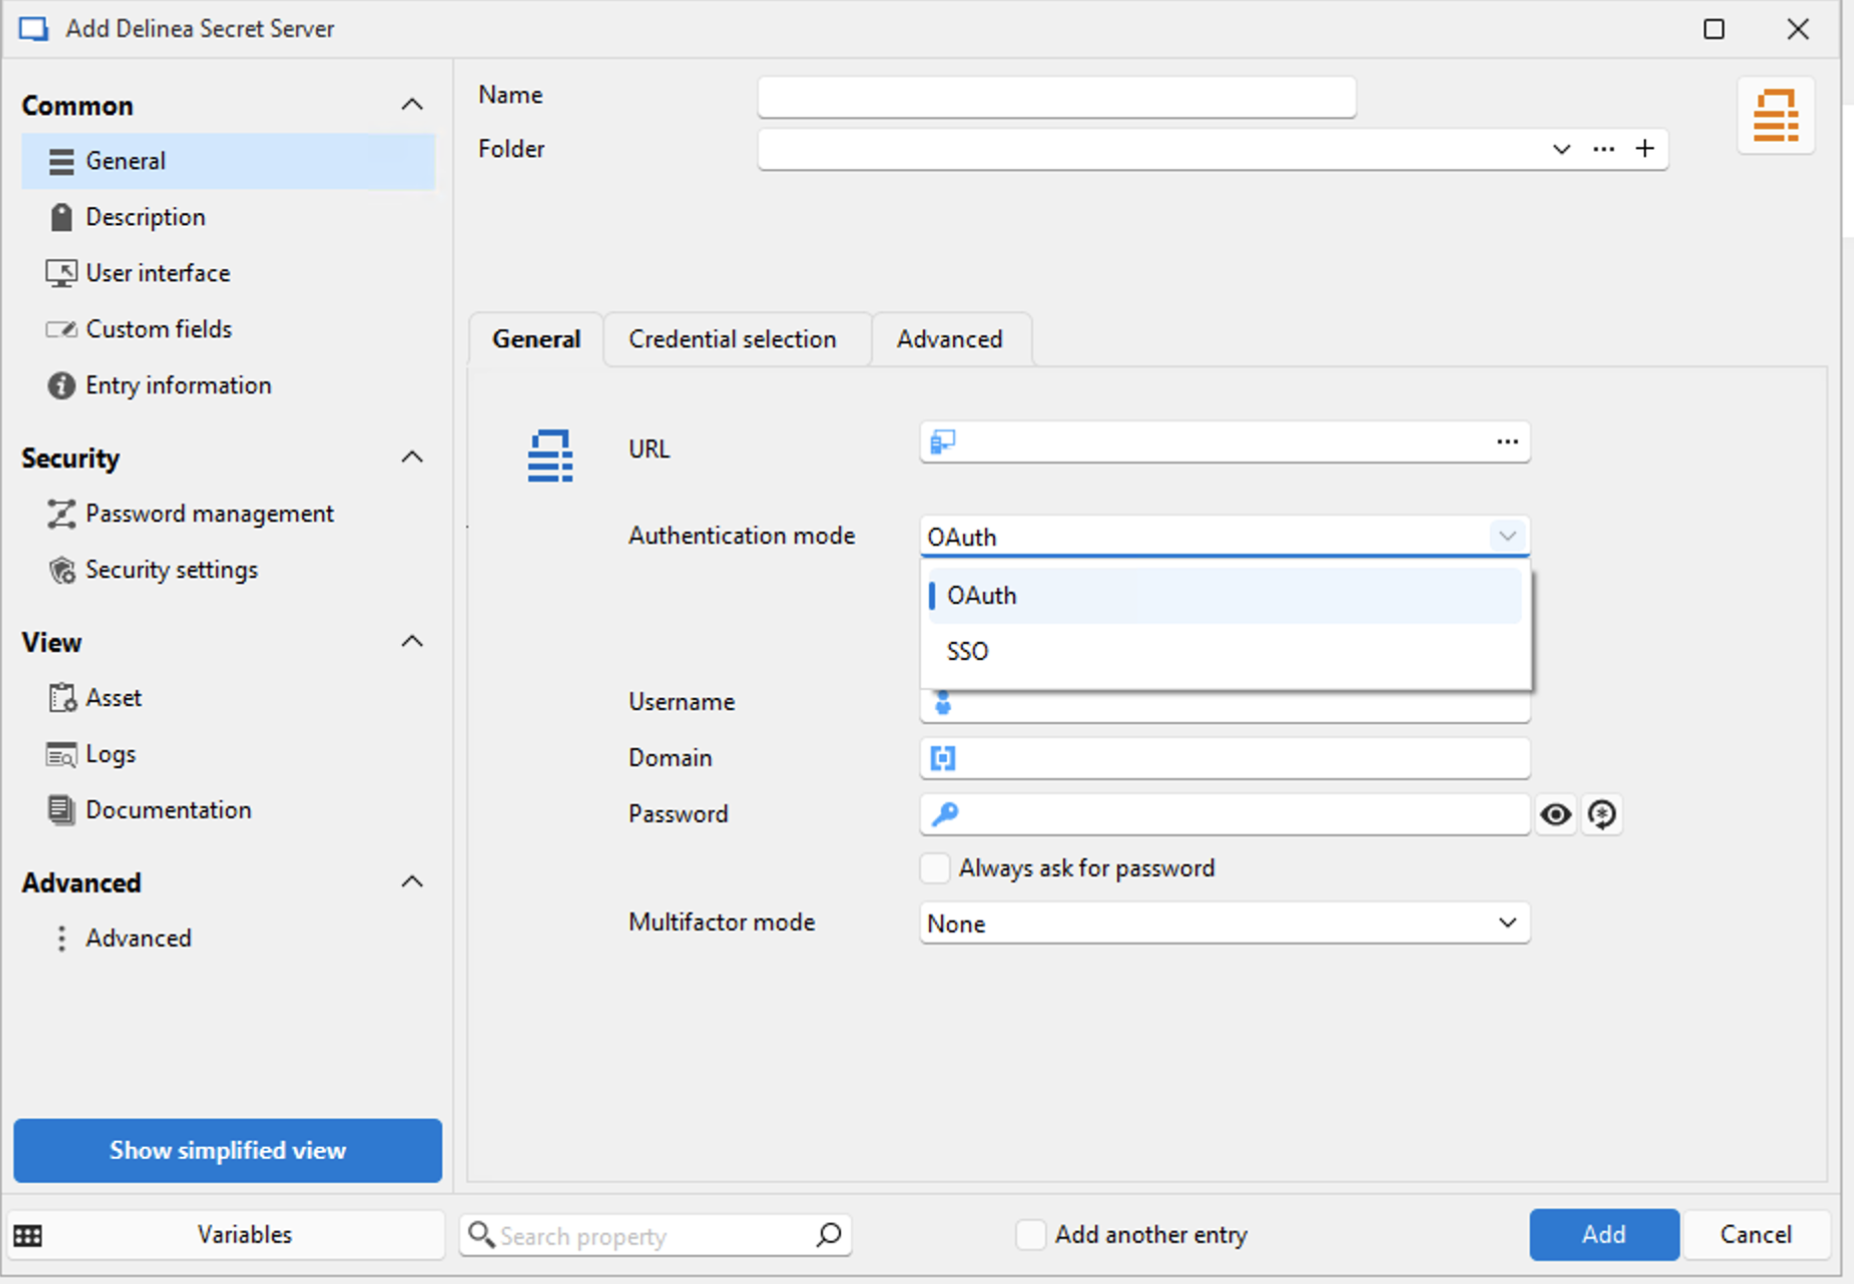
Tried both oAuth and SSO, none of the settings work.
Thank you in advance!