
juergengrabert
Gateway Revocation list is not in sync
We created a new CSR file using OpenSSL. We modified the JSON file.
We have a Devolution Server (Server1) and a Devolution Gateway (Server3). Server2 is the database.
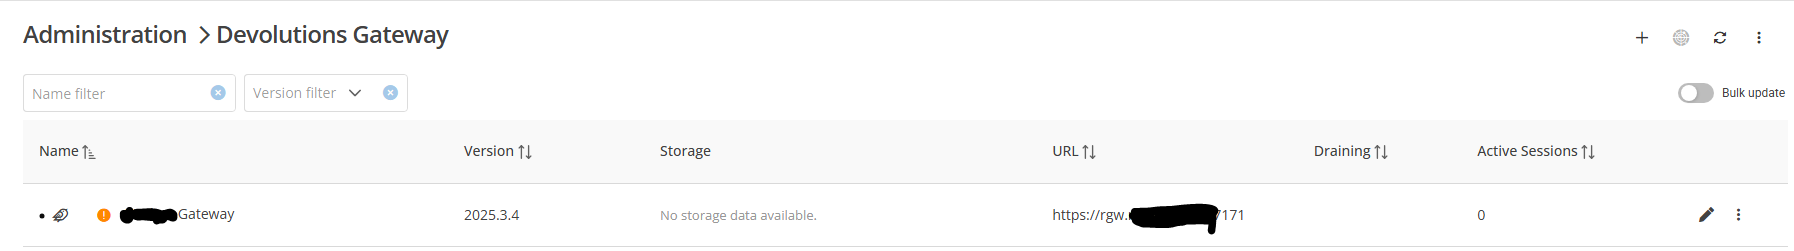
Configuration via the Devolution Server Console (Server1) is not possible because the Gateway doesn't appear there, only the server running IIS!
For whatever reason.
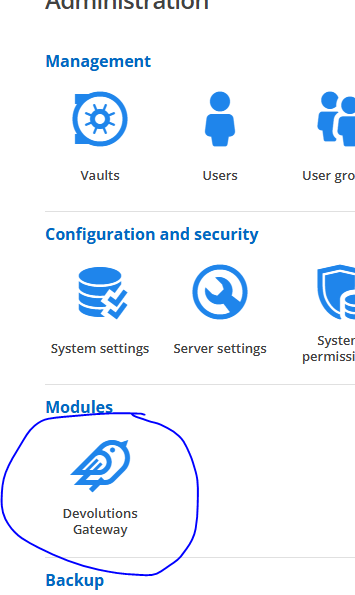
"Administration > Dev Gateway > Diagnostics" is accessed via the Dev Server.
Gateway Revocation list is not in sync
Hello,
we had to create new certificates for the gateway. These were signed by our CA. The Devolution servers are not in the domain, so we also had to store the root certificate locally. However, there is now a problem with the gateway.
The gateway is not accessible via Administration > Dev Gateway > Diagnostics.
It is running, though. The website (https) is also working.
The gateway log on the gateway server shows the following message:
"unauthorized at devolutions-gateway\src\middleware\auth.rs:189:28 [source: failed to verify token signature using main provisioner key, because signature error: invalid signature, because invalid signature]"
Do the Provisioner.PEM and KEY files also need to be recreated?
Regards, Jürgen
Gateway problem CertificateUnknown
Hi,
it´s working now. Our internal firewall blocked the contact to our CA. We put the certificate in the windows local cert store.
Thanks.
regards
Jürgen
Gateway problem CertificateUnknown
Hi,
there is a TLS Error. The certificate is not guilty.
Thanks
Jürgen
Gateway problem CertificateUnknown
Hello,
we have a little problem with a new Devolution Server / Gateway Installation. This is our first contact with the devolution software.
We want to use the GW to connect to several systems with rdp over "open in browser". In the GW LOG is the following error
devolutions_gateway::listener: handle_https_peer failed error="TLS handshake failed: received fatal alert: CertificateUnknown"
This is strange, the Devolutions Gateway Diagnose is ok and the certficate on the GW Server with https://GWname:7171 is also working.
The rdp target server message is
Failed to connect to wss://GWname:7171/jet/rdp (WebSocket is `Closed`)
Our devolution gw version is 2025.2.2
Regards
Juergen