
irisms
E-mail notification on Entry Expiration
Hi Maxime,
We're currently using "Custom" instead of "vault owner" as we don't want people to be able to export data.
For us, it would be ideal if we can use an AAD group (that's already synced to Hub). So if there is a change in ownership, then we don't have to adjust the report every tiem.
However the proposed solution could work for other companies I think. We just have a bit of a more specific setup.
Kr
Iris
E-mail notification on Entry Expiration
Thanks, that could already help us out!
But what we're really looking for is a scheduled report or notification on vault level.
We do have different vault owners and it is basically up to them to check whether their vaults do not have any expired or exposed credentials.
And it would be too time consuming for the administrator to check all our 2000 vaults. So, it would be great of the report could be set on vault level and then send to the vault owner(s).
Kr
Devolutions Cloud - Auto-assign licenses based on user groups
Hi,
we could use the feature as well were licenses, RDM in our case, could be assigned via groups of Entra ID. Not every user may have an RDM license, only consultants in specific teams/countries may have one. As you stated, Hub automatically assigns unused RDM licenses to whomever connects via RDM.
Now I have to manually check every couple of months if licenses aren't used by people who shouldn't have RDM.
Kr
Add expiry date SSO
Would it be possible to have a field where we see the expiry date of the client secret of the SSO configuration?
That way, we have a double check if the secret was correctly updated.
Automatically Refresh Web add-on
Hi Olivier,
that's correct.
Kr
Iris
E-mail notification on Entry Expiration
@Maxime,
any update on the PowerShell Script?
Kr
Iris
E-mail notification on Entry Expiration
Hi,
I wanted to support a-cjlin's request. I get this question a lot if there is a way to receive a mail or any notification when an entry is about to expire.
Preferably the system can send a notification to the vault owner and not only to the admin as we have over 1300 vaults with different people managing them.
Meanwhile I got the request today if it is possible to get the expiry dates via an API or PowerShell. Is there such an option available now?
Kr
Tags external and privileged
Hi,
as of this week, we have the possibility to add the tags “external” and “privileged” to a user.
I was wondering if it will be possible, in the future, to add the tag when inviting the user instead of waiting until the user accept the invite and then add the tag?
Kr
Iris
Create entry templates from scratch
Hi Maxime,
thank you for your answer. I didn't notice the custom one indeed.
I can work with that already but still it would be useful if we could build it ourselves.
Like some fields should be on the general tab and should be mandatory and now I have no option to do that.
Also if I want to adjust a template, I do not have an edit button. So, I need to delete it and start over again which is not very practical.
Kr
Iris
Create entry templates from scratch
Hi,
Within Hub you do not have the possibility to create entry templates from scratch.
You have to create a template from a predefined Devolutions templates, but that contains too many unnecessary fields for the templates we want to create.
It would be great if we had the predefined fields and some customer field so we can build or own template for certain things.
Is this doable?
Kr
Better permissions granularity
HI Sebastien,
Thanks for the info. Maybe a small extra request on this one.
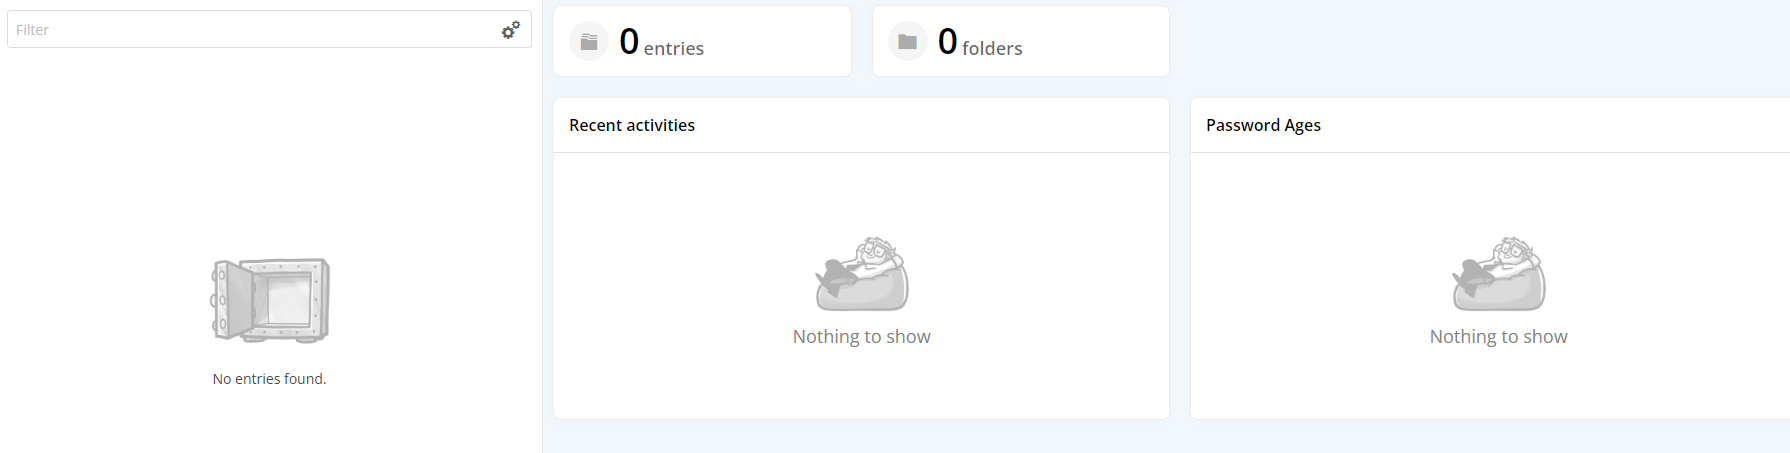
Would it be possible to have some sort of notification that you do not have the permission to view the content? Now it is just saying "nothing to show" of "no entries found" which is a bit confusing.
Users could think that there just aren't any entries in the vault instead of knowing that they just do not have access:
Automatically Refresh Web add-on
Hi,
When changing an entry on web application, this isn't instantly synced the web add-on.
People have to manually click on refresh in the add-on or open up a new browser session.
Is there a way this sync between those two can be automated, like syncing every hour or so?
Kr
Iris
Devolutions Cloud - Private Key Storage Method Enforcement
Hi Maxime,
I think this could be an interesting feature for us as well.
For us personally it would be easier as a global setting as we have over 600 users.
We're currently struggling a lot with users who did not pick mobile phone and then forgot their master password or lost their QR code and then we we have quite some work to get these users up and running again.
Kr
Iris
Created by if copied entry
Hi,
We have some colleagues that often copy entries instead of making new ones.
The only thing they find a bit strange is that the "created by" is copied as well. Since a person copied it, he is essentially making a new entry, so the "created by" should be the person who copied the entry.
Is this something that could be possible in the future?
Possibility to hide fields/collapse fields
Hi,
this is a great improvement indeed! Our end-users will be very happy about this.
Thanks!
Kr,
Iris
Possibility to hide fields/collapse fields
Hi
on an entry we have a sometimes a bit to much information which confuses an end-user a bit and doesn't see the password through all the other information. Would it be possible to hide some fields or collapse some blocks?
For example see this as one block and collapse it until we need it:

and have the possibility to hide some of these fields, maybe as a system setting:

Kind Regards,
Iris
Add Tags on vault level
Hi,
if we indeed could search on the description as well, that would solve our issue.
Thanks a lot.
Kind Regards
Iris
Add Tags on vault level
Hi,
currently it is possible to add tags on the entries within a vault itself and filter on it. But would it be possible to have this tag system on vault level? And off course filter/search on it.
The thing is that we have a lot of customers with very long names and we use an abbreviation as vault name. But then a user doesn't know the abbreviation and doesn't find the customer in the list of vaults. Or a customer recently changed names, we change the vault name, but some users weren't aware of it and don't find the vault anymore.
In that case, we could add tags with the long name or abbreviation or add the old name as a tag. Instead of adding everything in the vault name which sometimes results in very very long vault names.
Kr
Iris
Hide SSO groups in roles
For now, only SSO groups because we use them to onboard users on the application. Ideally you could say which groups can not be shown for non-admin users.
Kr,
Iris
Hide SSO groups in roles
We would like to hide the synced SSO groups for people who are not administrators. The reason for this is that we work with "vault" owners who are responsible for a vault and it is up to them to give the users the needed permissions like contributor or reader. But we really want them add permissions per person and not a whole bunch of
people who might not need access to that specific vault.
Better permissions granularity
Hi Maxime,
this is something we struggle with as well. We really need this one:
"The Observer permission should NOT be set on the vault itself, but on the folders. This way, you could be granted access to a vault, and see nothing in it, until someone gives you a observer/contributor/owner permission on a folder. Like you would with folders on your PC."
With this feature, we can regulate the access more on the "need to know" principle.
So I don't know if helps to move up the priority of this feature knowing that other companies struggle with this as well :)