Delinea Secret Server - "Refresh token" option seems not working and it keeps prompting credentials after token expiration
Delinea Secret Server - "Refresh token" option seems not working and it keeps prompting credentials after token expiration

Hi,
We are using currently 2026.1.14.0 64bit client under Windows 11.
We have implemented Delinea Secret Server solution with PAM distributed engines to be able to RDP connect onto our machines through PAM proxy, and it works great.
To be able to retrieve Delinea secrets info, we must first, for sure, provide Secret Server credentials when we launch the first related RDP session of the day and this part is working as expected.
At secret Server side, we've got this config :
Session Timeout for Webservices : 90 mins
Enable Refresh Tokens for Webservices : yes
Maximum Token Refreshes Allowed : 6
This should allow us not being asked for Secret Server credentials the whole day. But it seems not taking into account this "Enable Refresh Tokens for Webservices" option and prompts systematically to renter credentials for Secret Server login after 90 mins (then OK for the next 90 min and so on).
Could you check by your side or tell me what we miss, please ?
Thx
All Comments (7)
Hi Olivier,
Thanks for the details, that's helpful.
Could you check the following setting in RDM: File > Settings > Entry Types > Credential management > Delinea Secret Server, and see if "Save authentication token between sessions" is enabled?
If it's currently disabled, please enable it and let us know if you still get prompted for credentials after 90 minutes. If it's already enabled and you're still seeing the issue, let us know as well,
Looking forward to your results.
Best regards,
Samuel Dery
Hi Samuel,
Thx for this quick reply.
I don't get this option in my RDM current version (2026.1.14.0 64bit).
I only see this one, but doesn't change anything and, except if I misunderstand, not applying in our implementation context :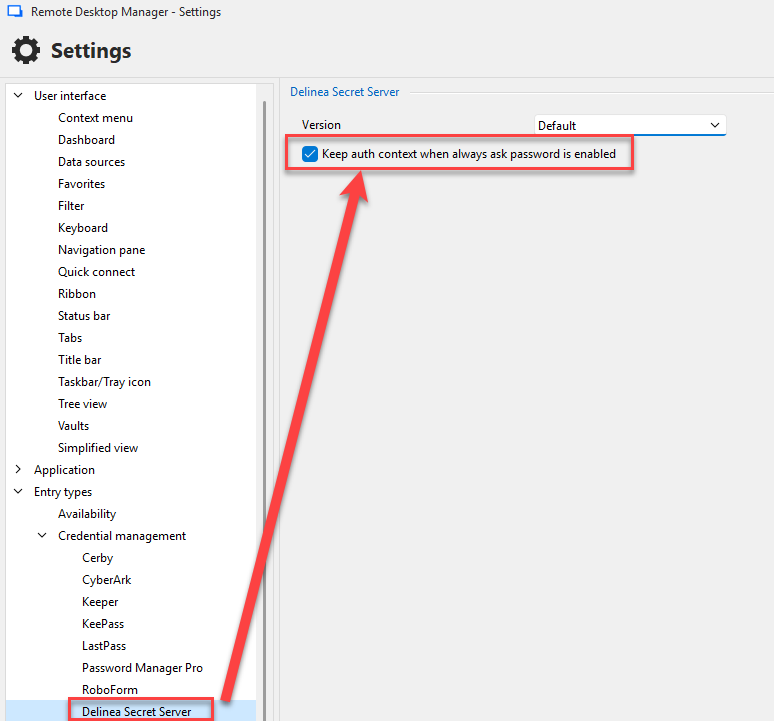
Kr.
078b086d-97f4-4b7d-b044-a3ce0963fdca.png
Hi Olivier,
Thanks for the details on your Secret Server configuration.
Before we dig further, could you confirm which type of workspace you are currently using with RDM?
https://docs.devolutions.net/rdm/getting-started/workspaces/workspace-types
Is there a specific reason why you are using version 2026.1.14.0?
Let me know,
Best regards,
Samuel Dery
Hi Samuel,
RDM DBs are hosted on MS SQL server 2025.
Regarding the version, we updated from RDM 2025 to 2026 because of the rebuilding of the Delinea RDP solution (currently 'common" RDP session while delinea specific on 2025) that allow more flexibility and variables usage. And the 2026.1.14 was the one available at this moment.
I requested some feature improvements to Devolution Support which will be available in 2026.3.4 it seems (and I'm going to request a new one), and I'm waiting it to be available to be able to test it before putting in prod.
Regarding this recurrent reauthentication problem, I modified the authentication method from SSO to OAuth in my Delinea Secrets, and used the "Delinea Secret Server" external credential to bypass it.
Now, with this config, the Delinea account password is only asked once a day (at RDM first start), then no more asked the whole day.
This is exactly what I expected as behaviour, so I won't investigate more on this.
Except if I miss something, I'm going to open a feature request to be able to manage this "External credential" using the Devolutions.Powershell module, cause it seems not possible currently (while the "My Personal Credentials" can be managed easily this way using the "get-RDMPersonalCredentials"). Is it correct ?
This point is important for me to be able to finalize the fully automated deployment of RDM profiles for all our operators.
Br.
Olivier.
Hi Olivier,
Glad to hear the OAuth + external credential approach solved the reauthentication issue, thanks for confirming what worked on your end.
Also, just as a heads up, RDM 2026.3 is planned for release this week.
Regarding your PowerShell question: you're correct, there is currently no cmdlet in Devolutions.PowerShell to manage the External Credential entry type. Get-RDMPersonalCredentials only covers My Personal Credentials, and there isn't an equivalent for External Credentials at this time.
Best regards,
Samuel Dery
Hi.
Just a follow up.
I'm testing the new 2026.3.8.0 RDM version (still on MS SQL Workspace), and the option "Save authentication token between sessions" is now available.
After tests, it didn't permit to solve our recurrent token refresh problem.
Anyway, as already mentionned, we'are now using the OAUTH Authentication with the "Delinea Secret Server" RDM credential, and it gives the results we expected.
Kr.
Hello Olivier,
We are happy to hear that everything is working as expected with the new configuration.
If you have any further questions, feel free to reach out.
Best regards,
Samuel Dery