RDM Hashicorp Vault Domain Prefix/Suffix

Hi,
before I dive into my question I want to explain our current situation to provide a better understanding about our issue:
We use RDM RDP objects to connect to our Windows servers. The credentials are provided within each RDP object. We would like to get rid of these credentials in RDM and utilize our Hashicorp vault instead. So far so good. The problem is, that our vault structure does not include the domain suffix/prefix. Therefore, the login to a domain joined server won't work.
Our current test scenario:
RDP object with linked credentials to Hashicorp vault
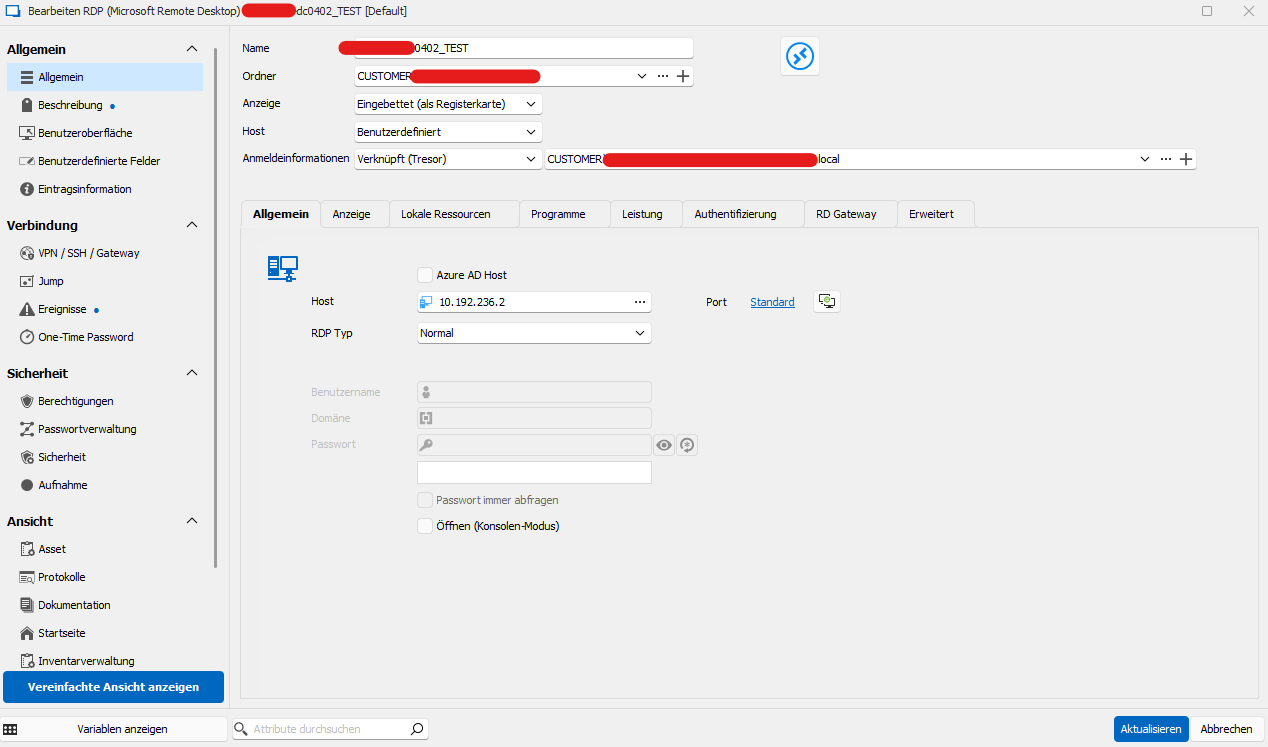
The credential object in Hashicorp looks like:
Path: XXXXX/CustomerID/ad (test.local)/Administrator/Administrator
As you can see, the user name itself does not contain any domain information. To make it work we would need to change the object to something like:
Path: XXXXX/CustomerID/ad (test.local)/Administrator/Administrator@test.local
Is there another way to tell RDM to use a specific domain without modifying the Hashicorp vault object? Any additional attribute or something like that? We want to avoid adding the domain suffix to all Hashicorp credentials as we have dependencies on certain automations.
All Comments (5)
Hello,
Is this domain in your case stored in the Hashicorp object? Otherwise, where is it stored?
Regards,
Hubert Mireault
Hi,
the domain is stored within the path: XXXXX/CustomerID/ad (test.local)/Administrator/Administrator