Problems with Roles - Cannot Add/edit/Delete

Hi,
I have just exported all data from my old RDM installation in to the new one, and though that Roles would be better to use when adding all new users. However, I'm having some issues with it.
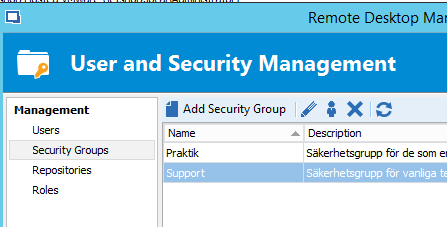
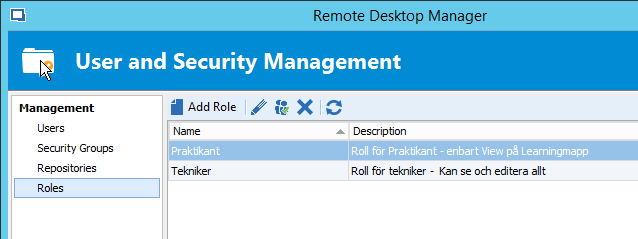
For example, I have two security groups created (Support and Praktik), and two roles created (Tekniker and Praktikant).
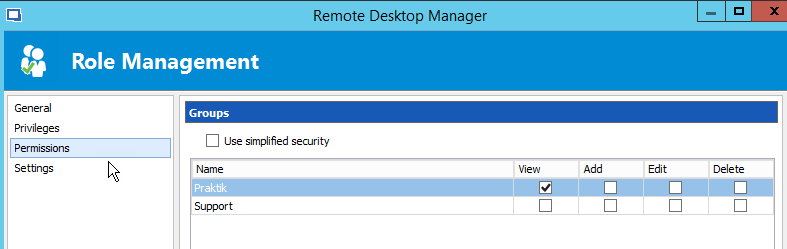
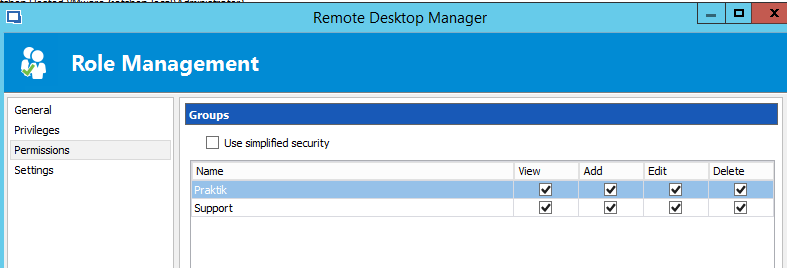
I have given the role Praktikant the permission View on the group Praktik, and given the role Tekniker View/Add/Edit/Delete on the group called Support and the group called Praktik.
Now, I have my own user created and added as member on the role Tekniker, but I cannot edit, delete or create any new entries in folders that have the security group set to Support.
I can manually override this by adding permissions manually on my user, but I'd prefer to have it done via Roles. Is this a known issue, or do I need to check the "Add", "Edit" and "Delete" under Permission->Rights for my user? I thought this was inherited via the Role I set up.
I have attached some screenshots below.
View of the Security groups:
View of the Roles:
SG for Role Praktikant:
SG for Role Tekniker:
Any ideas or suggestions?