Adding the possibility to unlock AD accounts during password reset
2 votes

Hello,
I'm opening this on behalf of user bdemsky in an attempt to reduce back and forth.
If a PAM Account is locked on ADDC due to too many failed logon attempts, it would be nice if "Unlock Account" was flagged when a check-in or password rotation occurs in the PAM module.
It would also be nice to improve the log in DVLS regarding this event so it's clear that this is what occurred as currently the log is generic.
I've attached screenshots of the current behaviour when an account is locked.

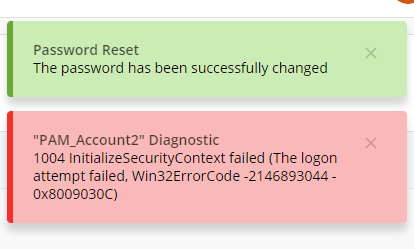
Error in text:
1004 InitializeSecurityContext failed (The logon attempt failed, Win32ErrorCode -2146893044 - 0x8009030C)
bdemsky, I invite you to continue this discussion if required.
Best regards,
Marc-Antoine Dubois
Marc-Antoine Dubois
All Comments (14)
Please also note that the notification for a password synch failure would also include the reason for the sync failure. In particular, if the account was locked.
thanks
Hello,
Thank you for your request. I will create a ticket in our backlog to improve the error message when the heartbeat fails. Additionally, I think it makes sense to unlock an account during the password rotation. I will discuss this with our security team to ensure it is not a problem, but it is likely something that can be done. We will post back here once we have an update.
Best regards,
François Dubois
I'll add my 2 cents here, the heartbeat failures when accounts are locked are really annoying, when migrating to prv accounts users tend to close the session without logging off, we are implementing automatic session timeouts but it's not always helpful.
As long as the password rotates unlocking shouldn't be and issue.
I'll even add to it if unlocking could be a seprate feature that uses the PAM abilities that would be awosome, so that I could delegate a team leader to be able to unlock his members instead of having to go through helpdesk and wasting time and resources.
Ben
Hello Ben,
Thank you for your input. Do you think that if we unlock the account during password reset, it would be enough ? With that, it would allow the user to force a password reset and the account would be unlocked. Would it work for you ?
Best regards,
François Dubois
It could be a good start but I don't think it would be the most convinient end product.
If a user has a few already opened sessions and was locked reseting the password would either cause him to lock up again more frequently from these active sessions or the user will have log off all active sessions and stop whatever he was doing.
Also it would require to do a check in and check out again, doubt they would even do that and just call helpdesk.
Thanks,
Ben
Hello Ben,
I understand your point. But I have one more question if you don't mind: Why an account that you just checked out would be locked ? Does the user try to change the password himself ? I just want to be sure that I understand your flow. Thank you in advance.
Best regards,
François Dubois
I'll give a general example of how it works why the locks are happening:
When a user authenticates to an AD joined server the current password is "cached" in a way for that session.
If while that session is active the password is then changed the session still uses the "cached" password.
If anything on that session tries to authenticate with AD it will get access denied, if it retries a few more times the accoutn will get locked.
So if a user already has active sessions to a server or more and changes the password without intiating a relog to these servers there is a higher chance for lockouts.
Before we started to use PAM accounts we were used to disconnecting from sessions and not logging out so we can return to what we were doing on a server.
After my team moved to PAM we had a TON of lockouts (sometimes every mintue) until we got used to logging out from most servers when we were done.
It's going to be the same for the users, we could unlock ourselves, they can't so even if they forget to log off from a single servers there may be random lockouts.