[any version] Adding administrator is to your identity disables all other roles
[any version] Adding administrator is to your identity disables all other roles
1 vote

Adding a "Role" to a user, should be additive, not 'ONLY', if you want ONLY we need a checkbox in the account that says user can only have these roles, otherwise it needs to be a way to say adding 'Administrator' to x user is an additional role they have.
All Comments (5)
Hi Matthew,
Thank you for reaching out!
I moved this thread to the feature requests.
We'll keep you posted with our thoughts regarding this.
Best regards,
Marc-Antoine Dubois
Hello @Matthew Morrow,
Can you confirm you're describing an issue in the Devolutions.PowerShell module (as opposed to, for instance, PowerShell Universal), and if so, which specific cmdlets it appears in? Both Add-RDMRoleAssignment and Add-DSRoleAssignment are supposed to keep a user's existing roles, so if you're getting a different behavior, we'll need to look into that.
Best regards,
Christian
@Christian Robert
It's my error. I accidentally moved the thread to the feature requests of the Devolutions PowerShell module instead of PSU feature requests. I moved the thread to the correct forum section.
Thank you.
Best regards,
Marc-Antoine Dubois
Hi @Christian Robert,
sorry to ask, but I'm confused. If the feature request is for PowerShell Universal, are you referring to the cmdlet or the GUI permission settings?
Since you are talking about a "checkbox", I assume you mean the GUI.
What is the desired behavior? Should adding the Administrator role remove all other roles, or should it be additive?
In the GUI, I don't see a problem because I can view all roles and decide which ones to assign.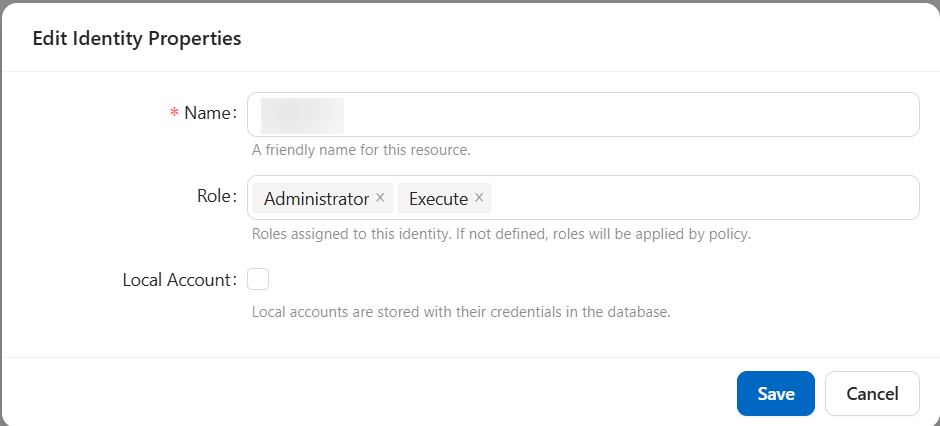
The available cmdlets are more problematic. Unless I'm missing something, permission assignment is done via Set-PSUIdentity, and this cmdlet only accepts a single role:
$identity = Get-PSUIdentity -Name 'testuser'
$roleAdmin = Get-PSURole -Name 'Administrator'

Set-PSUIdentity -Identity $identity -Role $roleOperator
f I want to assign both roles in code, I would need nested roles:
New-PSURole -Name 'AdminOperator' -Roles @(
    'Administrator'
    'Operator'
)

# Der Identity zuweisen
$identity = Get-PSUIdentity -Name 'testuser'
$role = Get-PSURole -Name 'AdminOperator'

Set-PSUIdentity -Identity $identity -Role $role
This is very inconvenient. I would have expected either an Add-PSURoleAssignment / Remove-PSURoleAssignment pair or for Set-PSUIdentity to accept an array of roles.
-Sascha Spiekermann
a0ecef4a-caad-4eda-a962-e49c90b88afe.png
Hello @Matthew Morrow,
Can you confirm you're describing an issue in the Devolutions.PowerShell module (as opposed to, for instance, PowerShell Universal), and if so, which specific cmdlets it appears in? Both Add-RDMRoleAssignment and Add-DSRoleAssignment are supposed to keep a user's existing roles, so if you're getting a different behavior, we'll need to look into that.
Best regards,
Christian
@Christian Robert
i am talking about going to the identity page, find the user, and add 'administrator' it blocks all other roles when you do that. i consider it a bug