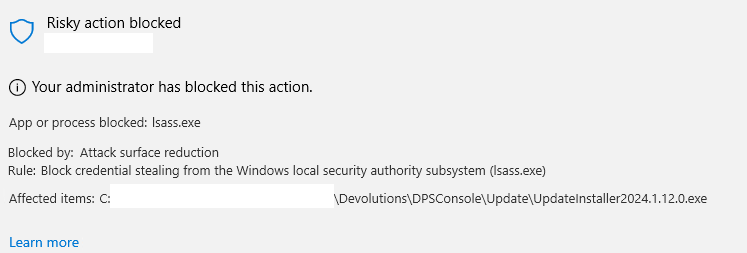
Do not use LSASS to retrieve credentials during update
0 vote

When updating devolutions server instance and scheduler the updater accesses LSASS.
This is a very well known attack technique used for lateral movement. https://attack.mitre.org/techniques/T1003/001/
It would be better if we did not have to make exceptions to our security to be able to update devolutions, and the updater fetches the credentials from somewhere that is not LSASS.