LDAP referals to unreachable child domain breaks PAM password reset/validation
LDAP referals to unreachable child domain breaks PAM password reset/validation

Hello,
When AD accounts in a parent domain are added to PAM from the results of a scan configuration, their password cannot be reset or validated if an unreachable child domain exists. The error message in the web GUI is 'An unexpected error occurred. The account can't be found on domain or domain unreachable'
A wireshark trace seems to indicate the communication stops when the LDAP search response from the parent domain provides a referral to the child domain which is not reachable.
Testing of the LDAP connection in the provider config for the parent domain also works, as does scan configuration.
Currently running DVLS 2023.12.0. The issue wasnt occuring previously, but unsure of the specific prior version that was installed when it was working.
Pls let me know if you would like any additional info.
Thanks
Joe
All Comments (17)
Hello,
Thank you for reporting this behavior.
We will need to configure such an environment internally to see if we can reproduce it.
On the other hand, our 2024.1 version contains a significant improvement that uses LDAP stack instead of LDAP Directory Entry.
Do you have the ability to create a staging environment to test our 2024.1 beta version to see if you get the same behavior? The following forum's post provides detailed information about this beta version that should be officially released in early March.
https://forum.devolutions.net/topics/41288/version-2024120-february-27-2024
Let us know if it's possible and what results you get. In the meantime, I'll ask our IT guys to get a domain structure to test it with 2023.3.12.0.
Best regards,
Érica Poirier
Hi Érica,
Thanks for your assistance. Unfortunately a staging environment is not available for testing this specific scenario. Also, its too risky to to deploy the beta version of 2024 to the production DVLS, but will likely upgrade soon after its officially released. Hopefully your team are able to reproduce the issue and formulate a fix soon.
Much appreciated
Joe
Hello Joe,
Our latest version has been available since Tuesday.
Let us know, once updated, if the issue still exists with the new LDAP stack our developers have implemented.
Best regards,
Érica Poirier
Hi Erica,
The issue is still occuring after updating DVLS to v2024.1.4
Joe
Hello,
Thank you for your feedback.
I'm sorry that the issue still exists.
Let me check with our developer team, and I will get back to you.
In the meantime, do you get any relevant error messages in the DVLS Logs?
Thank you for being so patient.
Best regards,
Érica Poirier
Hi Erica,
Nothing shows in the DVLS Console logs. In the Web GUI logs tab of the PAM account, it shows 'The account can't be found on domain or domain unreachable'.
Thanks
Joe
Hi Joe,
Thank you for your feedback.
Our developer and the QA team will investigate this issue. I'll get back to you once they provide any valuable information.
Thank you for being so patient.
Best regards,
Érica Poirier
Hello,
Thanks for your patience.
I have seen some odd behaviors with the provider when it is set with specific formats for the Domain Name and the username.
For example, a domain with a short format, like ACME instead of ACME.loc, could have similar behavior
With the username, when the domain is specified, either NETBIOS or UPN format, it can also have an undesired effect.
I suggest you double-check these, and if all fails, I think it would be appropriate to open a case and have a call to take a closer look.
Thanks for your cooperation.
Best regards,
Alex Belisle
Hi Alexandre,
Yes lets schedule a call to troubleshoot this pls.
In the provider config, the username is just 'username', no domain\ or @domain.local included. The 'test connection' on the provider works fine, and domain accounts are discovered via the scan configuration. The discovered accounts can be imported, but password reset and validation fails. Based on wireshark traces, it appears to be because of an LDAP referal timeout, because there is child domain in the forest which is unreachable from DVLS. It used to work fine in an earlier 2023.x version.
Thanks
Joe
Hello Joe,
I created a ticket on your behalf and have sent a link to book the support session.
Best regards,
Érica Poirier
Hello Joe,
I'm setting up a similar environment to attempt to reproduce the issue and I will fix it, I have a pretty good idea what the issue is. Feel free to reach out to me directly if you want to provide more information on your configuration. I'm also happy to attend the session with Erica.
Thanks,
Paul Dumais
Thanks Paul, appreciate your help. Lets chat on the meeting with Erica later today.
Joe
Hello Joe,
A fix for your issue has been implemented in the latest 2024.1.12 version.
Once updated, let us know if that works.
Best regards,
Érica Poirier
Hi Erica,
Thanks for the update. Unfortunately the issue is still occuring with 2024.1.12. Wireshark shows the LDAP communication stopping when a subdomain referal search response is received.
Possibly related, when using ldp.exe to replicate the LDAP search being done by DVLS, I noticed the tool locks up for a few minutes when I enable the option 'chase referrals'. Perhaps DVLS is also chasing the referrals and subsequently timing out or encountering some other error.
Joe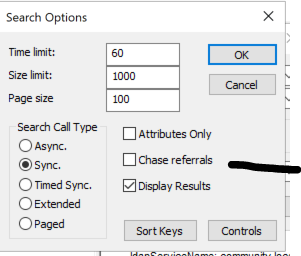
db241ad4-e221-4339-8239-a03f96a20627.png
Hello Joe,
We tried a simple referral following technique that we thought might work. I will send you a DM with some debugging tools so that we can figure out why DVLS is not chasing the referrals, maybe as you indicated it's a timeout, but we can debug it and figure it out once and for all.
Thanks,
Paul
We have resolved the issue. The problem was that the incorrect domain name was entered in the domain field and because this domain was not found, DVLS was attempting to try the first domain it found in the tree which was incorrect and attempting a redirect to an incorrect domain.
Paul
Thanks Paul.